Trusted execution environment
30
MENTIONS
13
EPISODES
12
PODCASTS
Search complete. 30 mentions across 13 episodes found for "Trusted execution environment".
Oct 15, 2026

speaker_0NARRATOR
The bank manager cannot inspect its contents.
speaker_0NARRATOR
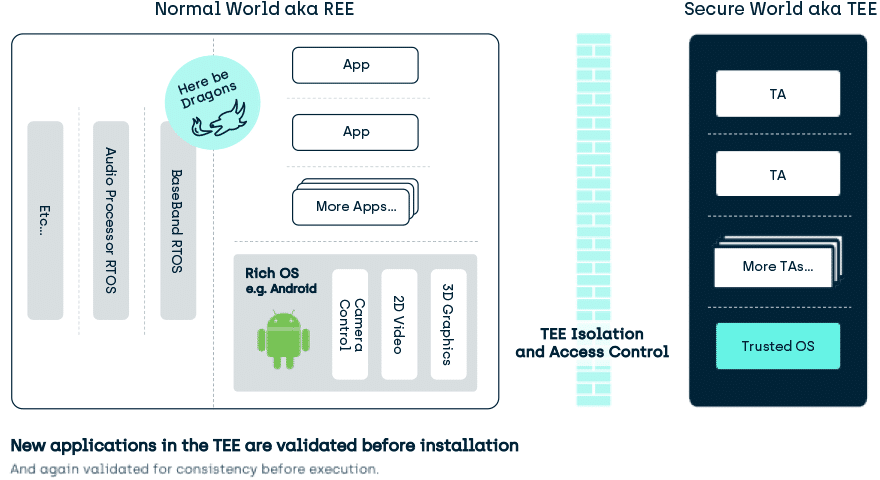
Using hardware-level trusted execution environments, TEEs, from AMD, Intel, and IBM, the processor encrypts the container's memory space using keys managed directly by the silicon.
speaker_0NARRATOR
The cloud provider hosts the infrastructure, but their hypervisor, host OS, and staff are cryptographically excluded from reading working memory.
speaker_0NARRATOR
Crucially, the industry is converging on open standards rather than proprietary SDKs.

Pascal HartigHOST
Right.
Emma ConnorGUEST
And on the iPhone platform, there's actually this Secure Enclave that lives inside the phone.
Emma ConnorGUEST
It's designed to resist even if somebody with millions of dollars and a fancy laboratory disassembles your phone and tries to look at what's inside.
Emma ConnorGUEST
It's designed to even then resist being able to pull any keys off the chip or bypass the rate limit that this chip enforces.

Jason SnellPANELIST
S-
Andy IhnatkoPANELIST
... and also, to be fair, part of the messaging that they have been d- d- promoting just, even just today is, like, the f- it's not in the first half of the press release, but the second half is all about everything is Secure Enclave.
Andy IhnatkoPANELIST
The microphone is s- uh, the audio from the microphone is Secure Enclave.
Andy IhnatkoPANELIST
The video is Se- Secure Enclave.
Andy IhnatkoPANELIST
Don't worry about having an open mic somewhere inside the house.
Andy IhnatkoPANELIST
So I'm sure that they want to be able to promise users buy a... [laughs] Not a...

Leo LaporteHOST
So-
Andy IhnatkoHOST
... and also, to be fair, part of the messaging that they have been d- d- promoting just, even just today, is, like, the f- it's not in the first half of the press release, but the second half is all about everything is Secure Enclave.
Andy IhnatkoHOST
The microphone is s- uh, the audio from the microphone is Secure Enclave.
Andy IhnatkoHOST
The video is Secure Enclave.
Andy IhnatkoHOST
Don't worry about having an open mic somewhere inside the house.
Andy IhnatkoHOST
So I'm sure that they want to be able to promise the users by, [laughs] not a...

Luca De GiglioHOST
But then you should probably don't trust verify, as we say in crypto, but then most people do trust and don't verify, which is kind of the weak part of the whole concept of like, I can verify what's happening, which doesn't mean I will.
Luca De GiglioHOST
So You probably need to have the knowledge in your company and the discipline to actually verify that this is the case, that they are not seeing what's happening with your data in their inference machines, right? When I talk about trusted execution environments, TEEs, it is not actually mathematical proof.
Luca De GiglioHOST
It is hardware attestation.
Luca De GiglioHOST
So now you're trusting the chip vendor, Intel, for instance, not trusting the software anymore.

Dustin DannenhauerHOST
No, no, I mean, it is, it is incredibly nuanced, and it's really good to be informed of all this.
Dustin DannenhauerHOST
You know, I got a chance to ask Joseph a question, and one benefit I think of using TEEs or these providers is that, um, so in the case where you might be worried...
Dustin DannenhauerHOST
Like, like so many times you're asking, um, for advice for these models.
Dustin DannenhauerHOST
Like, like you're like, "Here's things that I'm thinking about." Um, almost no individual can know the full extent of all laws and all jurisdictions.
Dustin DannenhauerHOST
There's this intense thing that like, okay, this is a service that you cannot, um...
Dustin DannenhauerHOST
Like even if that data kind of came out, it can't be held against you in like court.
Dustin DannenhauerHOST
And so that was something I kind of asked, like maybe that's one benefit of TEEs, for example, is to offer that, that guarantee, which you're not, you're-- My understanding is you're not currently getting that if you use like Anthropic and OpenAI.
Jesse PosnerHOST
Yeah.

Chris DalyHOST
We then developed a 10-layer security architecture for agentic AI.
Chris DalyHOST
We explored confidential computing and trusted execution environments.
Chris DalyHOST
And we examined some of the most difficult emerging attack surfaces, tools, runtime environments, persistent memory, and agent-to-agent communication.
Chris DalyHOST
But there is a problem.

R. Prescott StearnsHOST
Now, why does a simple reboot matter so much to digital forensics?
speaker_1HOST
To understand the genius of this defense, we have to look at the architecture of the secure enclave and how iOS handles encryption keys in memory.
speaker_1HOST
When you interact with an iPhone, it exists in one of two cryptographic states.
R. Prescott StearnsHOST
Okay, walk me through them.
R. Prescott StearnsHOST
But if the phone reboots, it shifts into the second state.
speaker_1HOST
Yes, the BFU state: Before First Unlock.
speaker_1HOST
In BFU, the encryption keys are purged from the quick access memory and are deeply locked inside the secure enclave processor.
R. Prescott StearnsHOST
So what does that mean for the phone itself?

Jeff CarlsonGUEST
...
Jeff CarlsonGUEST
the encryption and the, the Secure Enclave and..." Uh, and by then they've walked off, so it doesn't really matter.
Dan MorinHOST
[laughs]
Micah SargentHOST
[laughs]

Marcus RansomHOST
But I also think it's going to be interesting when people see exactly how this works.
Marcus RansomHOST
And I think there are some of the... requests where people are thinking that with secure enclave they're going to be able to unlock file vault with their idp which is not how this works not how any of this works but um you know i'm i'm looking forward to these features evolving throughout um you know, the 27 release, but I'm also excited.
Marcus RansomHOST
I have to say, I'm excited to see how many people are actually using platform single sign on now in production.
Marcus RansomHOST
So yeah.
Marcus RansomHOST
But when that light bulb goes off, it's spectacular.
Marcus RansomHOST
So, you know, this is something I'm going to be paying really close attention to.
Marcus RansomHOST
I'm really excited that Okta have now got Secure Enclave out there.
Marcus RansomHOST
Yes.
3 more episodes mention Trusted execution environment.
Create an account to see the whole feed, search across every transcript, and follow the entities you care about.