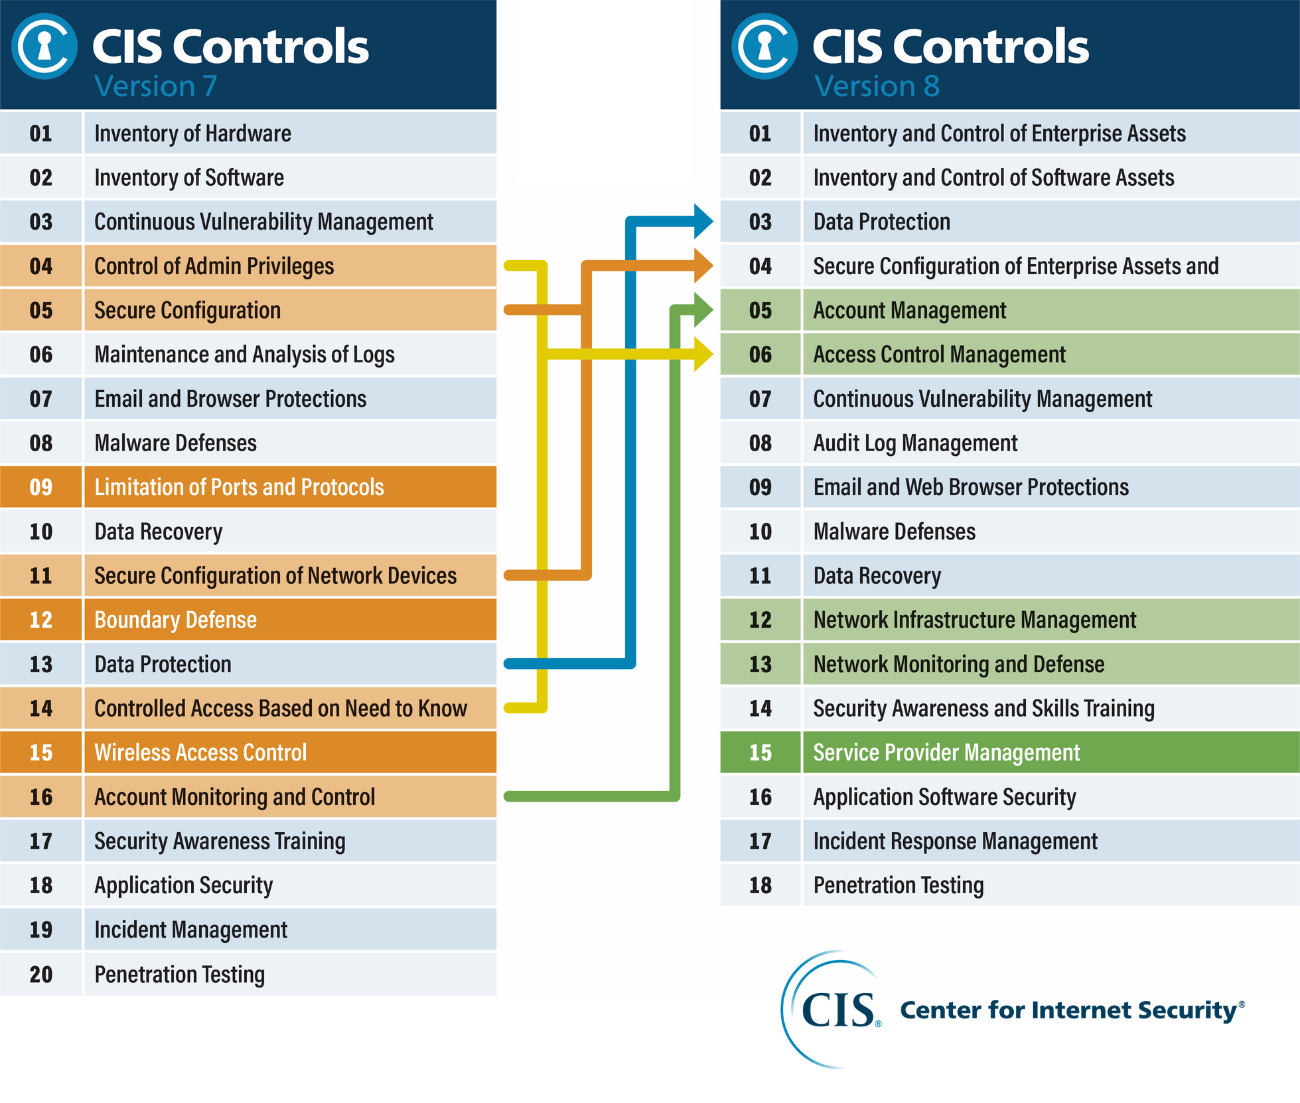
The CIS Critical Security Controls for Effective Cyber Defense
2
MENTIONS
2
EPISODES
2
PODCASTS
Search complete. 2 mentions across 2 episodes found for "The CIS Critical Security Controls for Effective Cyber Defense".
Sep 30, 2026

Sean AtkinsonHOST
Do we have foundational security elements already within the organization? Because adding that to a missing or a gap necessarily in your cybersecurity posture is not gonna be effective.
Sean AtkinsonHOST
You know, CIS, uh, Implementation Group one from the CIS Critical Security Controls is gonna build a foundational security element for you there, as well as others.
Sean AtkinsonHOST
NIST Cybersecurity Framework, following those tenants, um, have a lot of potency.
Sean AtkinsonHOST
And again, it depends on the parenthetic of your industry, right? The, you know, if we're looking at utility, if we're looking at healthcare, we're looking at, um, PCI requirements and things of that nature with those are ones that you want to integrate.

Sean AtkinsonHOST
Those are three separate areas, I think, as we move forward through our governance life cycle.
Sean AtkinsonHOST
'Cause in the first, you're looking at current business processes, right? And we'll think of non-AI interactive, so we've got, got privacy regulation, we have representative security controls, CIS controls, um, depending on the maturation or the size of the organization, depending on how far you're down that journey.
Sean AtkinsonHOST
We have a litany of other, um, acronyms that we could throw into the cybersecurity framework assessment.
Sean AtkinsonHOST
We have risk management and dependent upon quantitative, qualitative approaches in that space.