SAML
132
MENTIONS
43
EPISODES
39
PODCASTS
Search complete. 132 mentions across 43 episodes found for "SAML".
Nov 5, 2026

speaker_5HOST
Right, because you are taking the definitive record of your employees, their access tokens and your authentication logs, and you're just placing them on a third-party server.
speaker_6HOST
Yeah, usually relying on federation protocols like SAML or OpenID Connect.
speaker_5HOST
Where the cloud provider acts as the authoritative source and just passes certificates back to your local apps to grant access.
speaker_5HOST
But if that cloud provider suffers an outage, or worse, a breach, your entire digital infrastructure is basically paralyzed.

JoséeHOST
We're pulling from Microsoft's threat intelligence reports on the midnight blizzard compromise, plus highly technical intra-architectural documentation, CISA advisories covering the dark side ransomware incident, and the Ivanti Connect secure vulnerabilities.
Ernie PrescottHOST
Also, a pretty sobering 8K filing from T-Mobile and extensive threat research on golden SAML attacks.
JoséeHOST
And, you know, the connective tissue between all of those sources is the realization that the perimeter is no longer the primary battleground.
Ernie PrescottHOST
It's just not.
15 MINS LATER
JoséeHOST
It is practically the only reliable artifact an incident response team has to detect when a threat actor is scraping mailboxes via APIs using application impersonation.
JoséeHOST
If your enterprise does not have that specific purview telemetry enabled and actively feeding into your SIM, you simply do not have the architectural visibility required to see machine identity data exfiltration.
Ernie PrescottHOST
As you explain this, I can't help but compare it to another massive identity compromise vector we've seen, Golden SAML.
JoséeHOST
Oh, yes.

John DilgenHOST
Yeah, it's got to be impressive.
John DilgenHOST
Now, there are multiple attack chains, and the first one in this case exploited an unsigned SAML assertion with an XXE flaw.
John DilgenHOST
Now, in other words, not technical terms, this is just an XML vulnerability that can make an application reveal data it should keep private.
John DilgenHOST
And that allowed the attackers to access the cloud environment's internal metadata service.

Vincent De SmetGUEST
It's the same that you don't trust a network.
Vincent De SmetGUEST
Every packet carries... um you know authenticate well the packet it's more like in the protocol level the um authentication is sometimes injected by the like in in um in go teleport you can have an oidc provider so that it can you know with saml uh push through your identity so you log in once um and then your identity is propagated towards any service behind but you have to set up like a saml integration or a yeah yeah
Kai HendryHOST
yeah there's some Sort of, what do you call that?
Vincent De SmetGUEST
XML is the most annoying one because it's XML, but there's the other one, I think it's Jot, right? It's OIDC, so it's OIDC, yeah.

JohnHOST
Targets included pharmaceutical, telecommunications, semiconductor, and defense organizations, along with foreign ministries across Latin America, Europe, Asia, and the Middle East.
JohnHOST
An operator directed coordinated planner and worker agents to exploit edge applications through SAML and XML external entity flaws.
JohnHOST
The operation then harvested Active Directory credentials and searched for systems without monitoring.
JohnHOST
After gaining access, the adversary used DLL search order hijacking to deploy the custom BloodAlchemy backdoor that supported internal reconnaissance, credential theft, and command and control activity.
JohnHOST
Health ISAC recommends real-time EDR coverage across all hosts, strict SAML signature verification, metadata service protections, and least privilege cloud roles.
JohnHOST
Immediately rotate any credentials and cryptographic signing keys exposed through this activity.
JohnHOST
Now over to Rebecca for data breaches and data leaks with the compromise of customer secrets at North Flank.

Mirko PetersHOST
There was no reset email and no help desk ticket.
Mirko PetersHOST
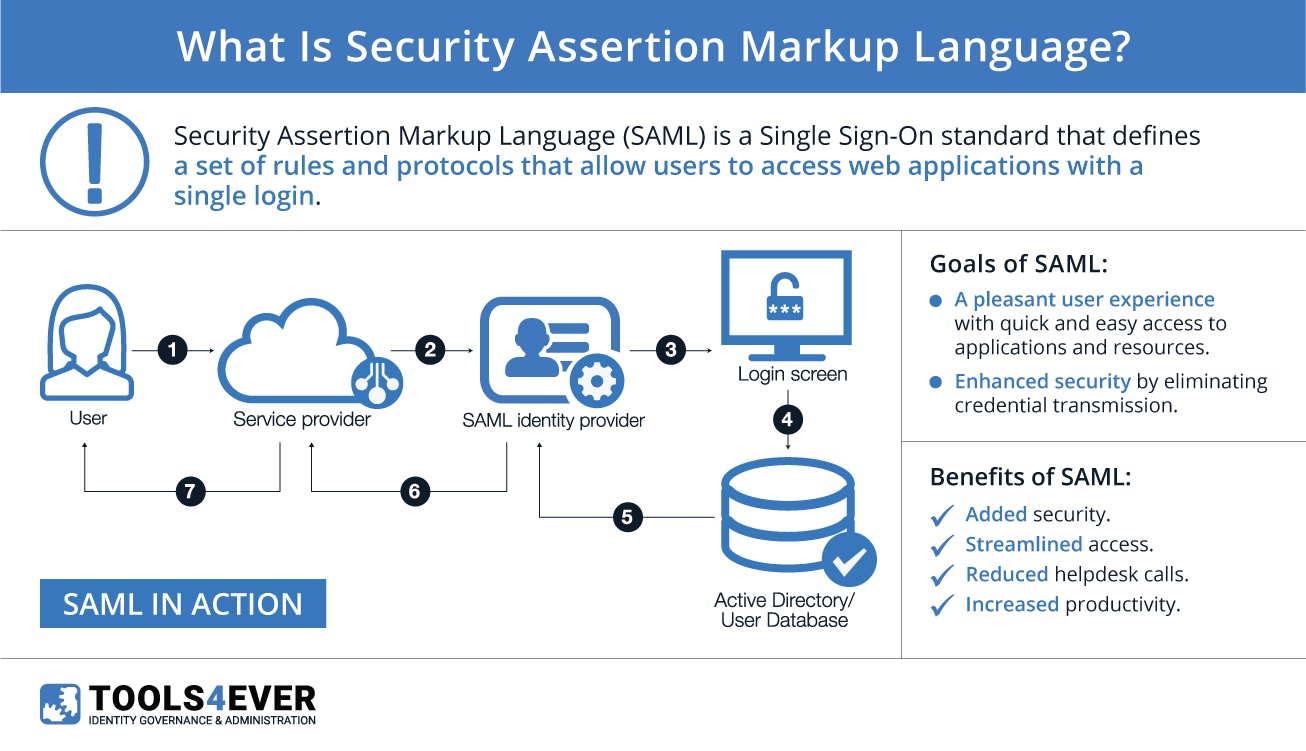
That quiet little moment is SAML, the standard that has been running behind corporate logins since 2005.
Mirko PetersHOST
By the end of this, you'll know what SAML actually is, how the handshake works, and the honest limits nobody puts on the sales slide.
Mirko PetersHOST
Welcome to the M365 FM podcast, where we explore the people, ideas and technologies shaping the future of work.
Mirko PetersHOST
That small moment plays out hundreds of times a day inside one company, and almost nobody stops to ask how it works.
Mirko PetersHOST
It just happens, and we move on.
Mirko PetersHOST
What SAML actually means? SAML stands for Security Assertion Markup Language, And that name is the least useful part of this whole story.
Mirko PetersHOST
Forget the words behind the letters and keep the idea.

Peter UllrichGUEST
And then you get managed CI with it, webhooks, all the good stuff, everything, all the features, basically.
Peter UllrichGUEST
And then moving on from individuals, I have organizations and they can be businesses, so like small or medium-sized businesses, and they would just have team plans where they don't get the SCIM, like automatic provisioning of accounts that you need for enterprise, SAML, like these kind of enterprise-y features.
Peter UllrichGUEST
They would fall out of the team plan, but team plan gives you an organization with private repos, enough minutes, CI minutes that you're fine.
Peter UllrichGUEST
And yeah, basically all you need as a business, right? And then enterprise is enterprise features, mostly authentication features, audit logs, and self-hosting as well.

Jonathan HarrisHOST
A network engineer who knows BGP thoroughly has the model write the Python that parses 40 router configs.
Jonathan HarrisHOST
An identity architect who can recite the auth specifications has it decode in an unfamiliar SAML assertion, then asks why it was built that way.
Jonathan HarrisHOST
They hold the why and hand over only the how.
Jonathan HarrisHOST
The historical parallel is well chosen.
Mirko PetersHOST
It's a live token, because a valid token can walk straight past the door.
Mirko PetersHOST
SAML versus OpenID Connect.
Mirko PetersHOST
Two systems can only talk if they share a language, and single sign-on has two big ones.
Mirko PetersHOST
The older language is SAML, which stands for Security Assertion Markup Language.
Mirko PetersHOST
It has been the workhorse of corporate login for well over a decade, and it wraps its messages in a bulky format called XML.
Mirko PetersHOST
SAML is good at carrying a lot of detail about a user, which is exactly what big companies wanted when they built their systems around it.
Mirko PetersHOST
That detail can include a person's department, their job title or the groups they belong to, and some apps use those details to decide what to show them.
Mirko PetersHOST
OIDC carries the same kind of information, but it packages it as claims inside a token instead of XML.

ElenaHOST
The techniques themselves were not exotic.
ElenaHOST
CrowdStrike says that in one intrusion, an unsigned SAML assertion combined with an XML external entity flaw was used to query cloud instance metadata.
ElenaHOST
In another, an unauthenticated orchestration service gave root access in a production container environment.
MarcusHOST
Unsigned assertions and unauthenticated services.
ElenaHOST
CrowdStrike's advice is practical.
ElenaHOST
Rotate signing keys and service credentials after any suspected exposure, including keys in historical backups and directory exports.
ElenaHOST
Enforce SAML signature validation and require IMDS version 2 on cloud instances.
ElenaHOST
None of which is new.
33 more episodes mention SAML.
Create an account to see the whole feed, search across every transcript, and follow the entities you care about.