Principle of least privilege
24
MENTIONS
7
EPISODES
5
PODCASTS
Search complete. 24 mentions across 7 episodes found for "Principle of least privilege".
Sep 17, 2026

Sec GuyHOST
The cryptographic proof eliminates plausible deniability.
Sec GuyHOST
This brings us to our core operating doctrine, least privilege.
Sec GuyHOST
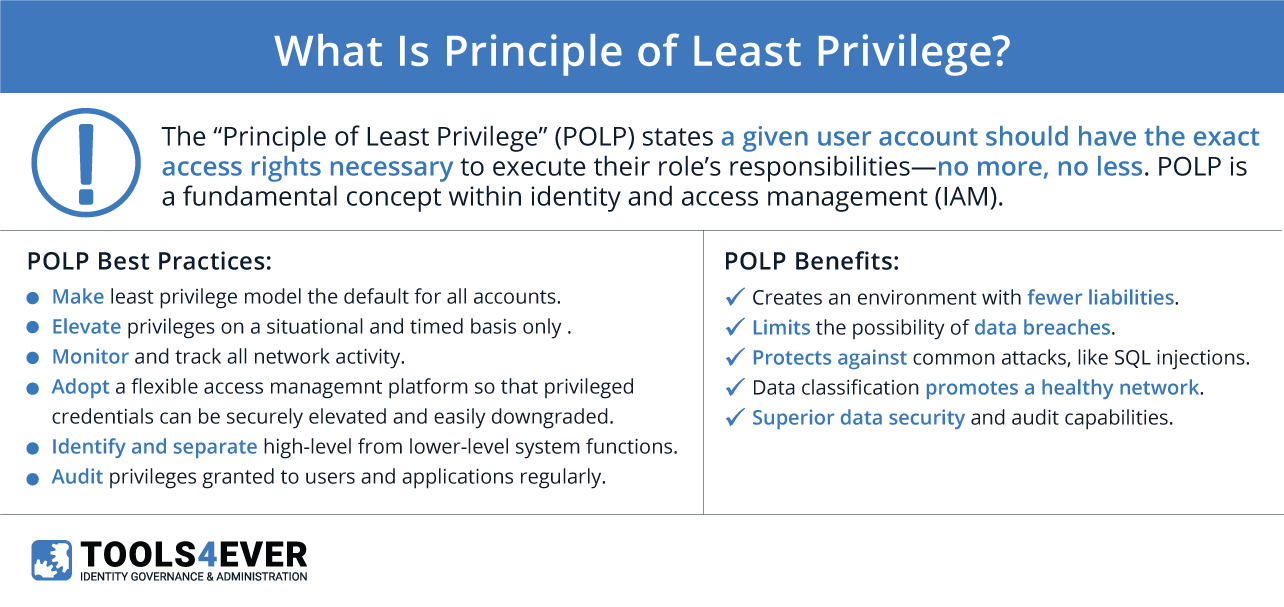
Lease privilege dictates that every user, application, and service account must operate with only the minimum permissions necessary to complete their job and strictly for the time needed.
Sec GuyHOST
If a junior analyst only needs read-only access to customer support tickets, granting them database administrator privileges is an architectural defect.
Sec GuyHOST
Because that instance had an IAM role with a policy that was too broad, the attacker was able to use the server's own identity to steal an API key from the metadata service.
Sec GuyHOST
This is why we follow the principle of least privilege.
Sec GuyHOST
Your policies should never use a wildcard asterisk to grant all permissions.
Sec GuyHOST
They should be granular.
Sec GuyHOST
They will show up on the test.
Sec GuyHOST
And the foundation, principle of least privilege.
Sec GuyHOST
Least privilege means giving users only the permissions they need to do their job, nothing extra.
Sec GuyHOST
This minimizes damage from mistakes or compromised accounts.

W. Curtis PrestonHOST
That cost them 400,000 euros in fines.
W. Curtis PrestonHOST
And when they appealed, the court basically said they didn't even try the concept of least privilege.
W. Curtis PrestonHOST
Today, that's what we're talking about.
W. Curtis PrestonHOST
Least privilege, best practices.
W. Curtis PrestonHOST
What does that mean exactly? And also, where do you start when everybody already has domain admin? Finally, we talk about role-based administration and why that's really the only realistic path here.
W. Curtis PrestonHOST
We talk about privileged account inventories, fire call accounts, segregation of duties, non-repudiation, and three backup roles that you should split apart before somebody quietly deletes your backup configuration.
W. Curtis PrestonHOST
My God, we've already spent 20 minutes on this.
W. Curtis PrestonHOST
So let's go.

Jason ElrodGUEST
So this is why it's essential that we give AI, especially ag- agents, their own identity.
Jason ElrodGUEST
That way, we can assign least privilege, ba- basically the minimum permissions necessary.
Jason ElrodGUEST
Segmentation is intensely important here, so only in the environments required for its function.
Jason ElrodGUEST
And I mentioned identity.
9 MINS LATER
Erica Spicer-MasonHOST
But I wanna give our, our listeners just kind of a forward-looking view of, uh, where this approach that we've talked today, whether that's segmentations, creating, you know, constrained or contained environments, w- where might that approach stop helping, and what risks would you leave listeners with to consider even after they've achieved the constrained access and segmentation?
Jason ElrodGUEST
Segmentation's critical, right? We, we've already mentioned that.
Jason ElrodGUEST
Least privilege, again, also helps dramatically reduce risk.
Jason ElrodGUEST
So segmentation and least privilege dramatically reduces risk.

Benny PoratGUEST
We need to make sure to deliver access to the business.
Benny PoratGUEST
But in the same time, we need, of course, to make sure for security perspective, to have least privilege.
Benny PoratGUEST
But at the same time, we are so lack of context.
Benny PoratGUEST
At the end, we are not running the business.
18 MINS LATER
Benny PoratGUEST
It don't know what it's going to use.
Benny PoratGUEST
So for sure, you actually want to restrict it.
Benny PoratGUEST
You want to start and just give it the minimum, the least privilege as possible.
Benny PoratGUEST
And least privilege is difficult.

Rob AllenGUEST
It's like, where does it, where do you draw, where do you draw the line? Where does it draw the line? Um, but yeah, as I said, sensible guardrails external to the thing itself, I think.
Rob AllenGUEST
Uh, I mean, it'll, it's, it's effectively the principle of least privilege, which is realistically best practices, or best practice for all security, you could argue.
Rob AllenGUEST
This is just another layer.
Tyler ShieldsHOST
Yeah.