Offensive Security
CompanyWikipedia
19
MENTIONS
4
EPISODES
4
PODCASTS
Search complete. 19 mentions across 4 episodes found for "Offensive Security".
Sep 16, 2026

Brittany GalliGUEST
There's a lot of companies that are just out there spreading the news, spreading the word of how cyber is transforming their entire technology or their companies.
Brittany GalliGUEST
OffSec being one of them is the one I've been looking at recently and working with.
Brittany GalliGUEST
And it's just...
Brittany GalliGUEST
It's a great place for, again, those in the career of security who maybe don't like exactly what they're doing today to head because it's not going to die if it's only going to get bigger.

Chris SchwenkHOST
All right, guys, we are talking about two incredible topics today.
Chris SchwenkHOST
We have an expert in the field as far as pen tests, offensive security, and ethical hacking.
Chris SchwenkHOST
He is also an expert in helping people kind of live in the post-resume world, and he's getting all his jobs from his social media presence.
Chris SchwenkHOST
His name is Phil Wiley, and he has almost three decades of experience in this field.
Chris SchwenkHOST
Yeah.
Chris SchwenkHOST
Can you go into those
Phil WileyGUEST
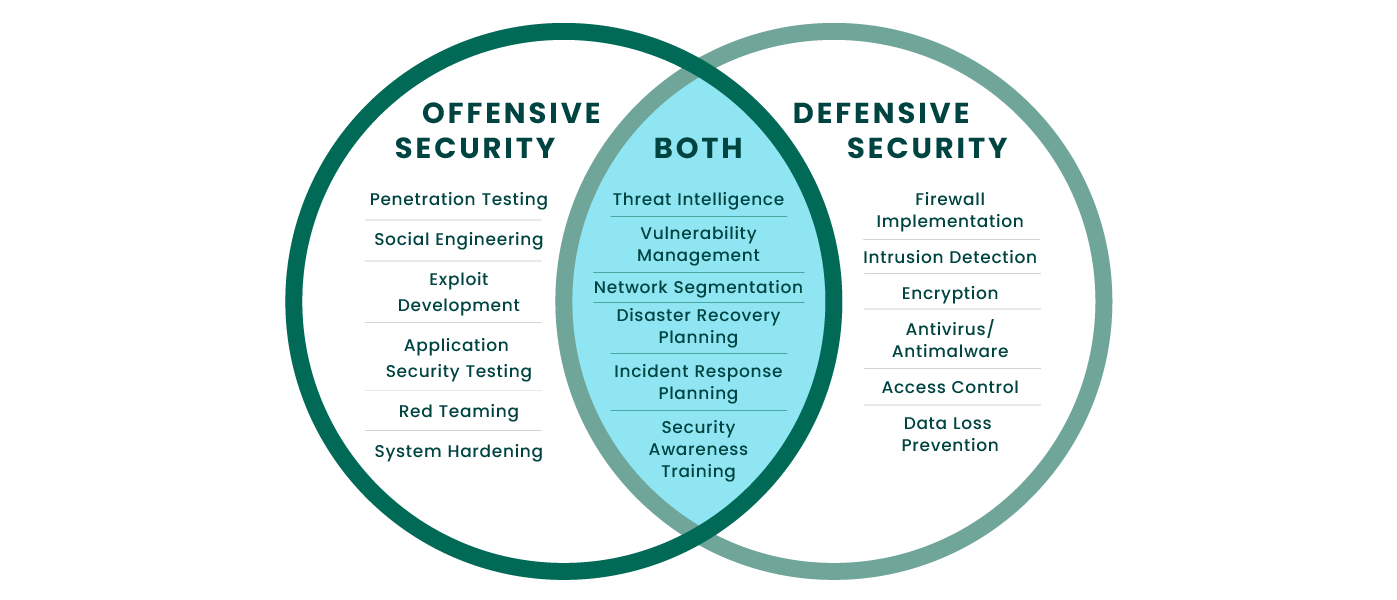
different teams? In purple teaming? So yeah, the red team is more generically used for the offensive security side.
Phil WileyGUEST
The true definition of a red team operation is you've got a group of people that they try to get in to the organization, see if they can breach it to, to lead, you know, exploit vulnerabilities to breach the organization.

William WrightGUEST
Some are not.
William WrightGUEST
So things to look out for would be like OWASP, perhaps SAN accredited testers, OFFSEC accredited testers, In the UK and the EU, there's others versus the US, but really looking to see that a methodology has been applied that can be referenced somewhere in the real world and not just randomly put together.
William WrightGUEST
Another thing that we see quite often is the IT service provider, especially if it's a subcontracted IT service provider or an MSP, conducting the pen tests themselves against the estate that they support.
William WrightGUEST
And that's like marking your own homework.

BruceHOST
That reminds me of...
BruceHOST
There's this one that keeps getting advertised from Offensive Security.
BruceHOST
Offensive...
BruceHOST
It's called...
BruceHOST
It's like AI red teaming from offensive security.
BruceHOST
And you've got to take AI 300.
BruceHOST
And you've got to take the OSCP before you can take this test.