NIST Cybersecurity Framework
22
MENTIONS
20
EPISODES
19
PODCASTS
Search complete. 22 mentions across 20 episodes found for "NIST Cybersecurity Framework".
Nov 2, 2026

speaker_0HOST
Makes sense.
speaker_1HOST
And the book really highlights the value of leveraging those established security standards, things like the NIST cybersecurity framework.
speaker_1HOST
That's a widely adopted set of cybersecurity best practices and standards.
speaker_1HOST
And it's like a yardstick you can use to measure and communicate risk across the organization.

Scott ChristensenHOST
Like that's a very mature compliance program versus the average customer.
Scott ChristensenHOST
We just talked about NIST CSF.
Scott ChristensenHOST
It's 135 control questions and it's pretty, pretty lightweight.
Scott ChristensenHOST
It's six function categories.

John VerryHOST
So how robust is it? Like, you know, so what are some of the, like from a cybersecurity requirements perspective, what does it encompass? Did they Did they kind of go their own way being its government? Did it kind of align with NCSF? What'd they end up doing?
Jeremy PriceGUEST
Yeah, this is one of the more annoying things to me in the jobs that we're in is that the government can't find a way to take something like NIST CSF or ISO 27001 and say, let's apply this because organizations are under multiple regulations typically.
Jeremy PriceGUEST
We've got, if you're in energy, for instance, you might have TSA pipeline security directive that you have to follow.
Jeremy PriceGUEST
Well, they've got their set of guidelines and now these guidelines also do not follow a standard framework.

Jason WebbGUEST
Yeah, so that's like a subset of something that's related to my work.
Jason WebbGUEST
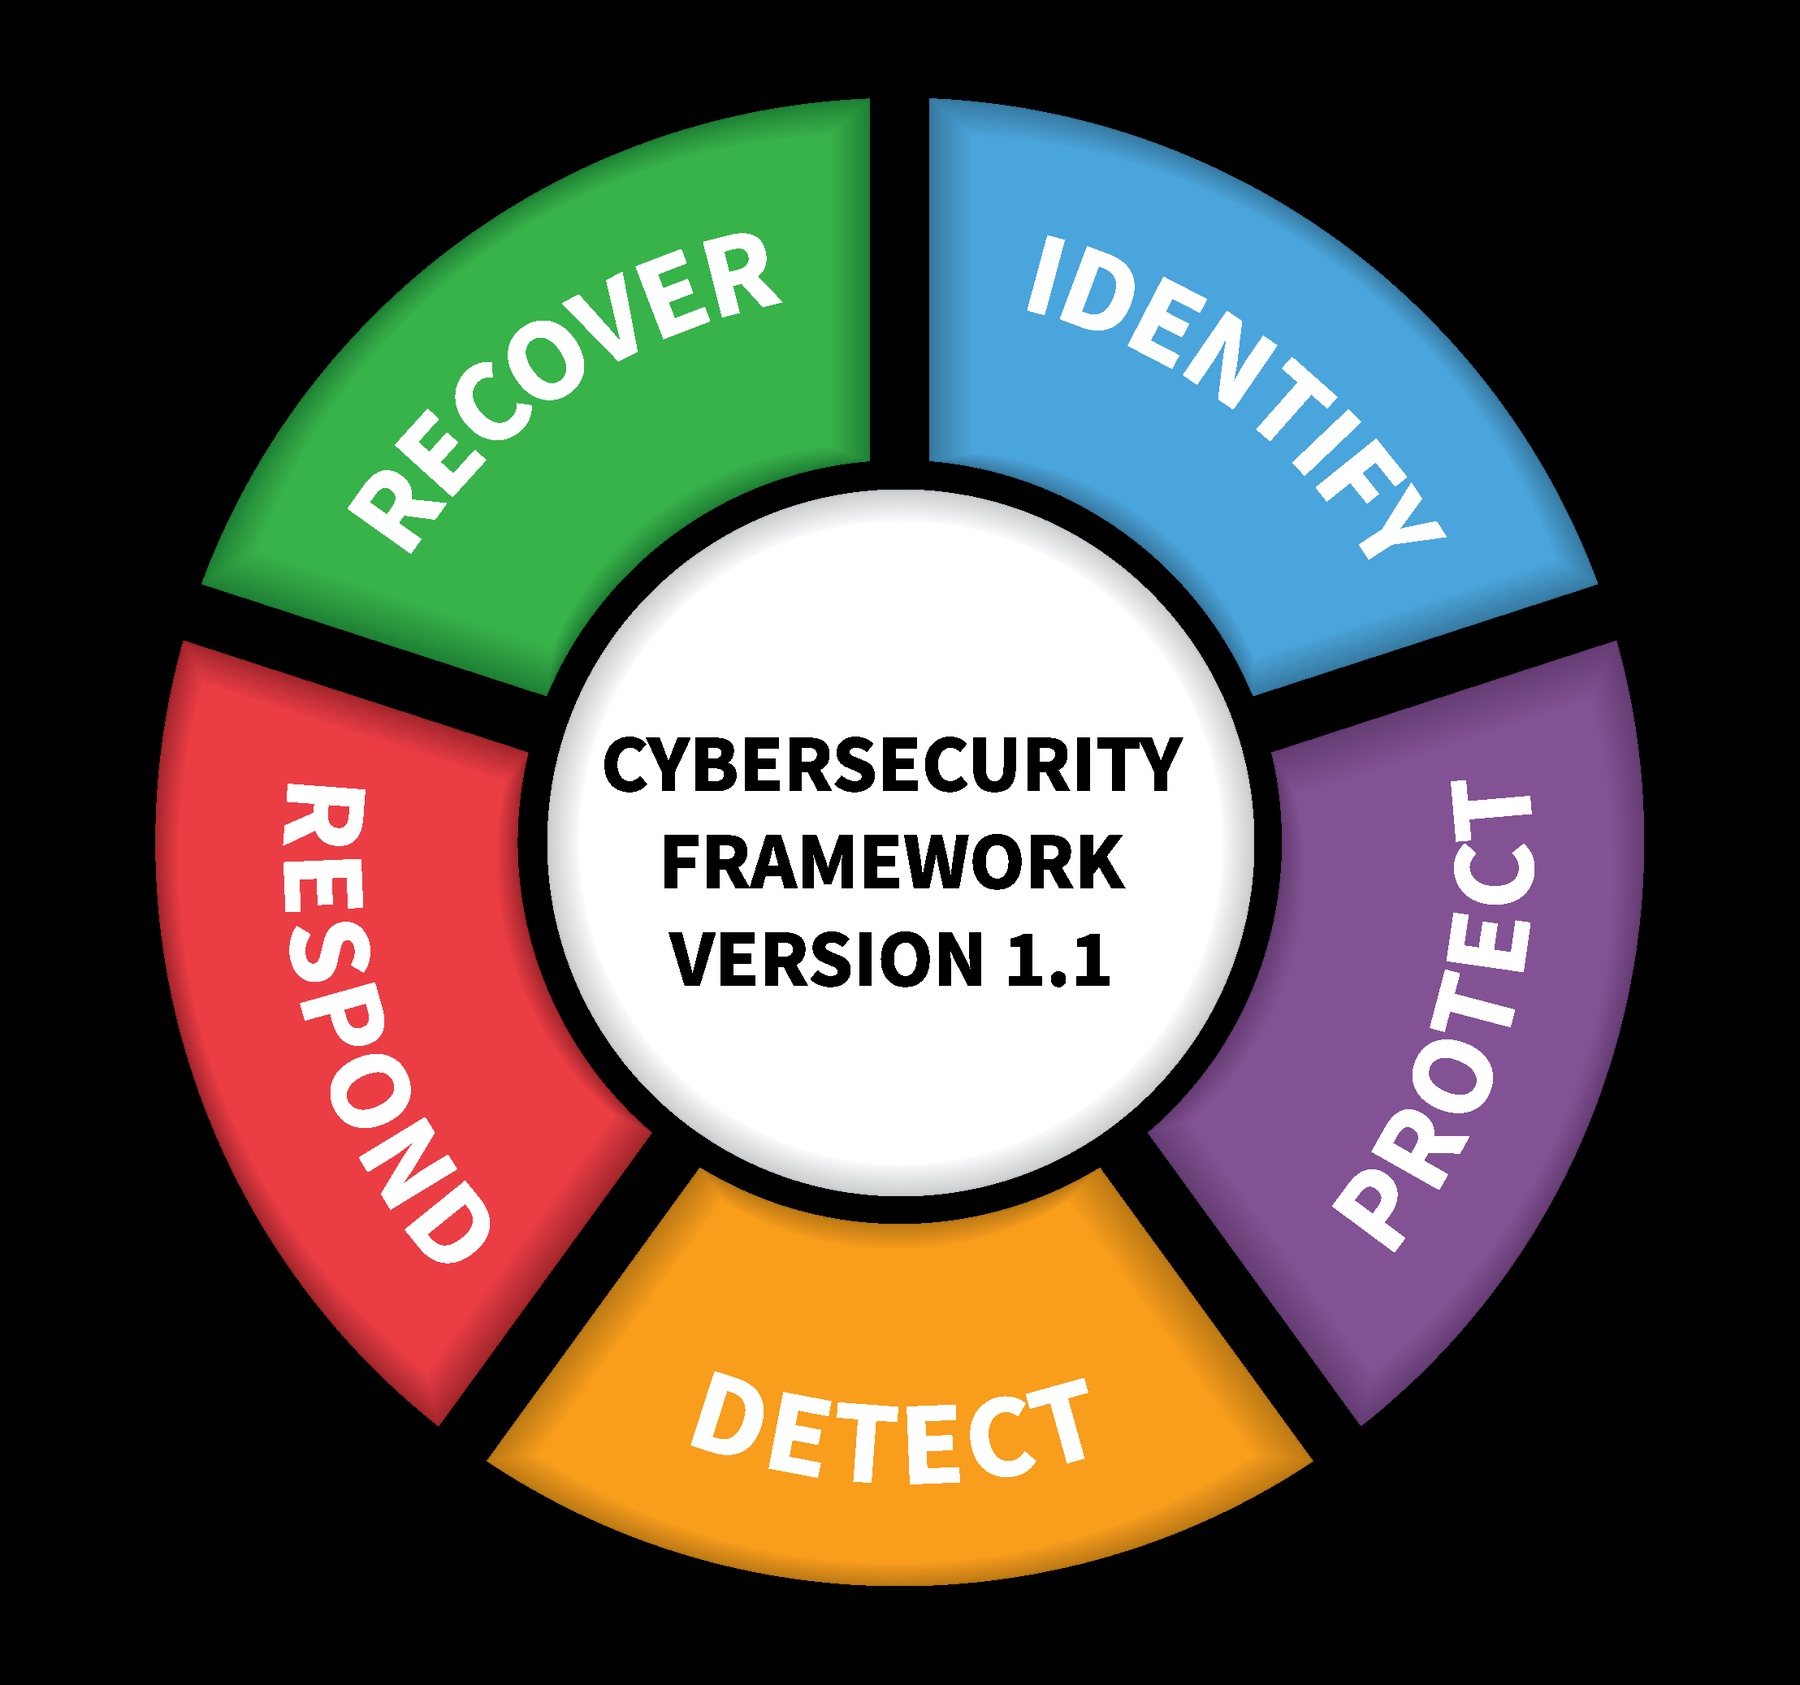
So there's something called the NIST Cybersecurity Framework, and it's identify, protect, detect, respond, recover.
Jason WebbGUEST
And it's basically just a framework for dealing with building out a cybersecurity program, right? We identify our risks.
Jason WebbGUEST
We have protections in place to protect against them.

speaker_0HOST
So on these also, they will not ask you what are the different categories or theme in the NIST AI Act.
speaker_0HOST
Even they were not asking for the previous NIST CSF also.
speaker_0HOST
They just want to know that these frameworks are there.
speaker_0HOST
And as such, all the topics which you see in the exam, they are coming from these frameworks only.

Kenneth BibleGUEST
And they're all going to be able to see that maturity level go up.
Kenneth BibleGUEST
And so that really, and it actually played in later on in the update to the NIST cybersecurity framework.
Kenneth BibleGUEST
If you recall, the NIST cybersecurity framework was updated.
Kenneth BibleGUEST
They started with a new pillar.
Kenneth BibleGUEST
called governance.

Lisa DarganGUEST
These tools can be very effective to help you manage that overhead, but it's about you managing that overhead and managing the compliance and integrating frameworks together, then it is about necessarily, oh, I'm going to bring that because it's going to make my life easier on day one, isn't it?
Wayne ArmstrongGUEST
Yeah, because if you've ever manually tried to map 27001 to NIST CSF to PCI, et cetera, it can be very confusing where if you set it up in the tool, it's all done for you.
Lisa DarganGUEST
Yeah.
Lisa DarganGUEST
Okay.

Jonathan PouletGUEST
IT side.
Jonathan PouletGUEST
Yeah, if you're coming from the IT side and you're a cybersecurity professional and you're familiar with other frameworks like NIST 800-53 or the NIST CSF framework, you're going to already know a lot of the concepts that you're going to see in the ISA IEC 62443.
Jonathan PouletGUEST
Now, what you will see that's different is the unique aspects of these standards that apply to whether you're an asset owner If you work for a chemical plant or a manufacturing company, there are parts of that standard that apply to you and your responsibility.
Jonathan PouletGUEST
And if you're a supplier supplying equipment into that asset owner, there's parts that apply to you.

Jonathan PouletGUEST
IT side.
Jonathan PouletGUEST
Yeah, if you're coming from the IT side and you're a cybersecurity professional and you're familiar with other frameworks like NIST 800-53 or the NIST CSF framework, you're going to already know a lot of the concepts that you're going to see in the ISA IEC 62443.
Jonathan PouletGUEST
Now, what you will see that's different is the unique aspects of these standards that apply to whether you're an asset owner If you work for a chemical plant or a manufacturing company, there are parts of that standard that apply to you and your responsibility.
Jonathan PouletGUEST
And if you're a supplier supplying equipment into that asset owner, there's parts that apply to you.

Jonathan PouletGUEST
IT side.
Jonathan PouletGUEST
Yeah, if you're coming from the IT side and you're a cybersecurity professional and you're familiar with other frameworks like NIST 800-53 or the NIST CSF framework, you're going to already know a lot of the concepts that you're going to see in the ISA IEC 62443.
Jonathan PouletGUEST
Now, what you will see that's different is the unique aspects of these standards that apply to whether you're an asset owner If you work for a chemical plant or a manufacturing company, there are parts of that standard that apply to you and your responsibility.
Jonathan PouletGUEST
And if you're a supplier supplying equipment into that asset owner, there's parts that apply to you.
10 more episodes mention NIST Cybersecurity Framework.
Create an account to see the whole feed, search across every transcript, and follow the entities you care about.