Nessus
Computer programWikipedia
37
MENTIONS
25
EPISODES
20
PODCASTS
Search complete. 37 mentions across 25 episodes found for "Nessus".
Nov 18, 2026

Dan DeClossGUEST
And you can't rely on other vendors to do that as part of their products either.
Dan DeClossGUEST
Like, you know, obviously like Nessus or Tenable or whatever scanning vendor you're using, that can identify that software, but it's not, its job is just to identify vulnerabilities and track them.
Dan DeClossGUEST
It's not necessarily, storing that information for later use.
Dan DeClossGUEST
Now, they may continue to evolve, but I think you need a centralized platform that is actually saving all of this information and automatically updating the asset inventories for software so that you can then, as soon as it comes out, it's like, okay, show me the assets that have PHP installed on them.

Katie MoussourisGUEST
I was a molecular biologist and worked on the Human Genome Project And during that time when I was working at MIT on the Human Genome Project, we were getting hacked a lot.
Katie MoussourisGUEST
So even before it was really a job description, I took it upon myself at MIT to start defending our networks and start scanning us for known vulnerabilities using some early versions of Nessus way back in the day and some other scanners.
Katie MoussourisGUEST
And then I was trying to patch us up as best we could to avoid getting hacked constantly while working on the Genome Project.
Phillip WylieHOST
That's a really cool story in your entry point, working at stake and hanging out with the loft people.

Adrian SanabriaHOST
And Bug Bounty is one of those.
Adrian SanabriaHOST
It's mostly vulnerability management, kind of traditional Nessus Rapid 7 Quala stuff.
Adrian SanabriaHOST
But I do take apps that calls in Bug Bounty calls every now and then.
Adrian SanabriaHOST
And this is one that has popped up quite a bit this year is, okay, now with AI, like, can I just do this myself? Do I still need a bug bounty program? Do I need to attract other people to look at my stuff and find bugs? So I'm thrilled to have this conversation today.

Adrian SanabriaHOST
And bug bounty is one of those.
Adrian SanabriaHOST
It's mostly vulnerability management, kind of traditional Nessus Rapid 7 Quala stuff.
Adrian SanabriaHOST
But I do take apps that calls in bug bounty calls every now and then.
Adrian SanabriaHOST
And this is one that has popped up quite a bit this year is, okay, now with AI, like, can I just do this myself? Do I still need a bug bounty program? Do I need to attract other people to look at my stuff and find bugs? So I'm thrilled to have this conversation today.

Adrian SanabriaHOST
And bug bounty is one of those.
Adrian SanabriaHOST
It's mostly vulnerability management, kind of traditional Nessus Rapid 7 Quala stuff.
Adrian SanabriaHOST
But I do take apps that calls in bug bounty calls every now and then.
Adrian SanabriaHOST
And this is one that has popped up quite a bit this year is, okay, now with AI, like, can I just do this myself? Do I still need a bug bounty program? Do I need to attract other people to look at my stuff and find bugs? So I'm thrilled to have this conversation today.

Adrian SanabriaHOST
And Bug Bounty is one of those.
Adrian SanabriaHOST
It's mostly vulnerability management, kind of traditional Nessus Rapid 7 Quala stuff.
Adrian SanabriaHOST
But I do take apps that calls in Bug Bounty calls every now and then.
Adrian SanabriaHOST
And this is one that has popped up quite a bit this year is, okay, now with AI, like, can I just do this myself? Do I still need a bug bounty program? Do I need to attract other people to look at my stuff and find bugs? So I'm thrilled to have this conversation today.

Network ChuckHOST
This one is cool because it's very revealing.
Network ChuckHOST
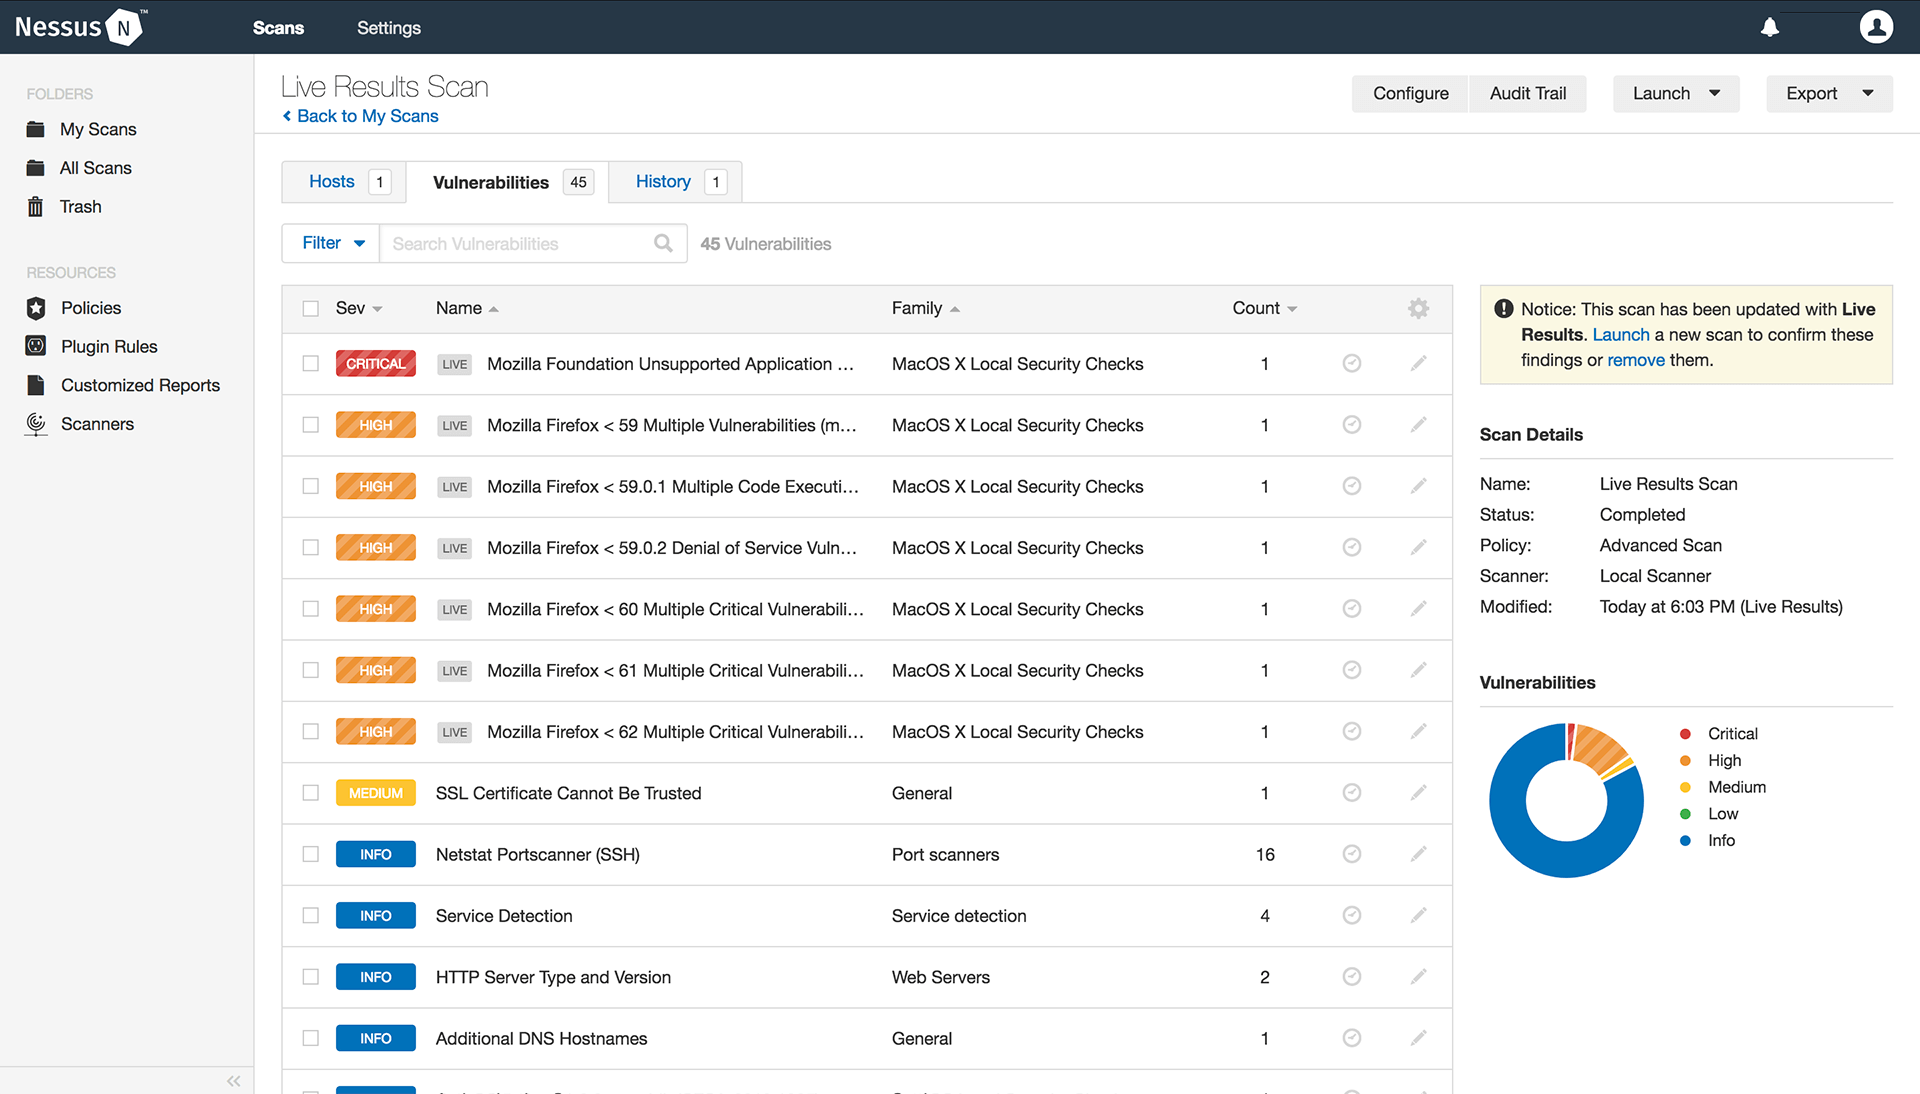
What is this? In title we're including the Nessus scan report.
Network ChuckHOST
Nessus is a vulnerability scanning tool.
Network ChuckHOST
It'll scan your system and tell you how you're vulnerable.
Network ChuckHOST
And we're searching for that in the title.
Network ChuckHOST
And then the keyword, this file was generated by Nessus.
Network ChuckHOST
So just scrolling through here, like let's see parkland.edu. We've got their Nessus scan and we can see, hey, maybe they have some vulnerabilities that we can possibly exploit.
Network ChuckHOST
And it's just in a nice format for us.

Russ GleberGUEST
My personal opinion, it's one that Breachlock shares as well, but regulators and compliance frameworks have evolved to cover AI-assisted offensive security, but I hope that they make human in the loop and human accountability mandatory as they update their policies and their controls.
Russ GleberGUEST
If we don't make human in the loop or some sort of human accountability mandatory, we end up right where we were for the past 15 years with a whirlwind of vendors and MSPs just running a NASA scan, slapping the results onto a pen test report and making a quick dollar in the market because they know pen testing is a commodity.
Russ GleberGUEST
That's my personal opinion.
Russ GleberGUEST
That's what Breachlock shares as well.

Rohit NambiarGUEST
executed on a given system get back results see all right so this worked that didn't work i need to tweak this i'm going to run this again kind of in that what is considered a genetic workflow execute and these frameworks also are of different sophistication levels right initially we saw something like heck strike which was a little bit more of a a more simpler MCP server, if you will, right? It was more that you had an LLM and you could point it to this server that the LLM could speak with, right? And the server just had tools sitting on it.
Rohit NambiarGUEST
It had Nmap, it had Nessus, it had pen testing tools or red teaming tools that everyone knew of.
Rohit NambiarGUEST
And essentially, you could run the tool.
Rohit NambiarGUEST
It returns a result.
15 more episodes mention Nessus.
Create an account to see the whole feed, search across every transcript, and follow the entities you care about.