JSON Web Token
61
MENTIONS
35
EPISODES
25
PODCASTS
Search complete. 61 mentions across 35 episodes found for "JSON Web Token".
Sep 24, 2026

Justin BrodleyHOST
Azure Front Door edge actions are now available to you.
Justin BrodleyHOST
Uh, this supports edge actions, letting customers run JavaScript at the edge to inspect and manipulate requests before they hit the origin, including header manipulation, origin override logic, and lightweight JWT claims checking.
Justin BrodleyHOST
Edge actions are managed as standard lone Azure resources, uh, configured via Azure portal REST API or PowerShell modules.
Justin BrodleyHOST
The runtime is intentionally minimal with no outbound network access, no crypto libraries, and a 10-millisecond execution limit with fail-open behavior, meaning errors or timeouts result in requests passing through unprocessed.
Ryan LucasHOST
Safe
Justin BrodleyHOST
...
Justin BrodleyHOST
this makes it suitable for claims pre-filtering, uh, but not full JWT signature validations.
Justin BrodleyHOST
Because edge actions cannot cryptographically verify tokens, actual authentication must still happen at the origin or another trusted gateway.

Herman PoppleberryHOST
Post bodies survive.
Herman PoppleberryHOST
JWT claims survive.
Herman PoppleberryHOST
Any non-standard auth header survives.
Herman PoppleberryHOST
So you get a file that feels clean.

speaker_0NARRATOR
You are hired as a junior security analyst for a startup that publishes a public REST weather API.
speaker_0NARRATOR
This API exposes endpoints such as get/weather?city=, get/forecast?lat= and lon=, post/users, registration, post/login, authentication with JWT, get API keys, management of consumer API keys, and a premium tier accessible via API key plus rate limiting.
speaker_0NARRATOR
The API relies on a back-end service, a cache layer, Redis, a relational database, PostgreSQL, and calls one external third-party meteorological data provider.
speaker_0NARRATOR
The company wants a complete threat model before starting any pen test in order to prioritize security tests and corrections.
speaker_0NARRATOR
This mini-project directly reinforces the skill block, understand the risks of an application to prioritize tests and corrections, and prepares the pen test blocks that follow.
speaker_0NARRATOR
Scope.
speaker_0NARRATOR
In scope, all public and authenticated endpoints, the JWT auth/session flow, API key management, the cache and database interactions, and the outbound call to the third-party weather provider.
speaker_0NARRATOR
Out of scope, exploitation/live pen test.
CornHOST
And bearer tokens make it worse because they're inherently relayable.
CornHOST
There was a good discussion around Agent Passport earlier this year making the point that if Agent A presents his JWT to Skill B, Skill B can reuse that token to call Skill C while pretending to be Agent A.
CornHOST
Nothing stops it.
CornHOST
The token doesn't know who's holding it.

George FletcherGUEST
Another problem is that OAuth access tokens, which were sort of the way, if the inbound request was from, let's say, a mobile app or some other client, and you sent in the access token and then you use the access token within your network, right? A couple of things often happen.
George FletcherGUEST
One, lots of people were not using JWT based access tokens or ones that were adjacent and signed.
George FletcherGUEST
So you had to go back to the authorization server to validate the access token at each workload.
George FletcherGUEST
So that was one piece of it.
Jeff SteadmanHOST
What is a transaction token? Just
George FletcherGUEST
plain terms.
George FletcherGUEST
Plain terms, a transaction token is technically a signed JWT, and it's intended to represent the transaction that's being requested.
George FletcherGUEST
So that could be something like transfer $100 from this account to that account.

Johannes UllrichHOST
Today, we have news of a much more popular framework, the Isabel framework, which is used, uh, to control, uh, PBXs, basically phone systems, via web applications.
Johannes UllrichHOST
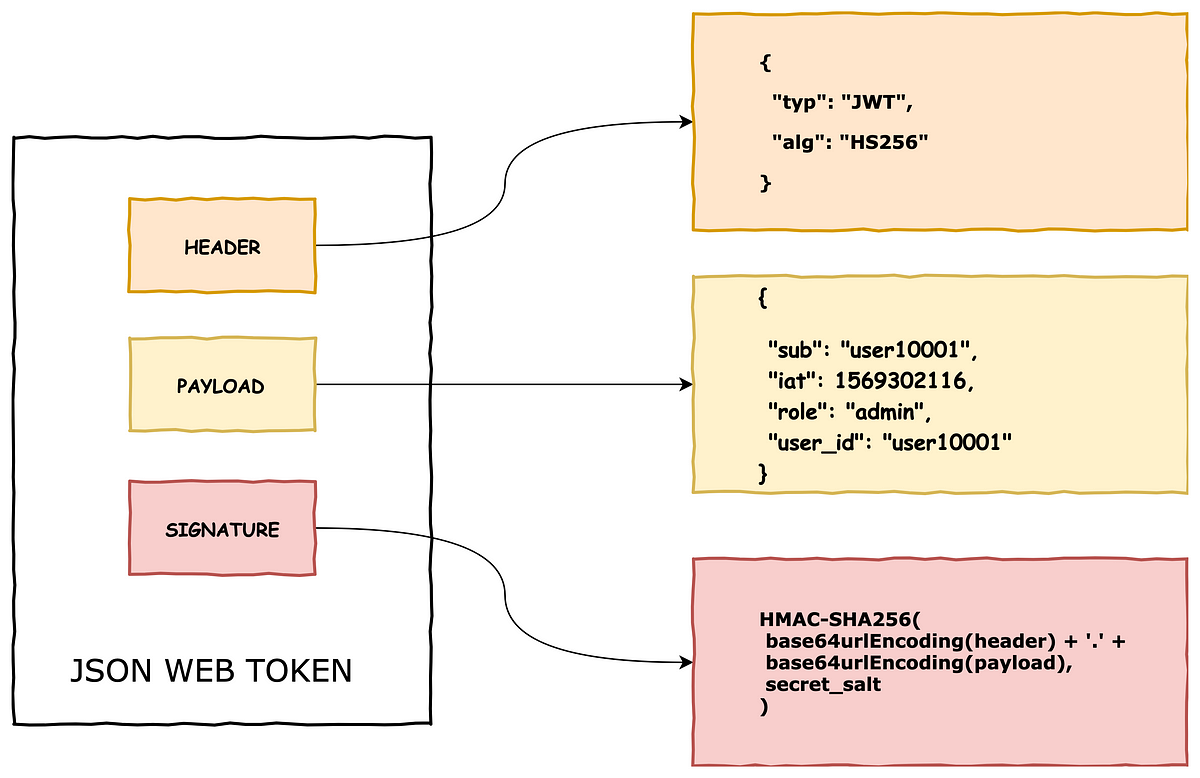
Well, uh, this particular framework contained a hard-coded JWT key, so basically the secret key being used to sign these JSON web tokens.
Johannes UllrichHOST
With that key, it was possible to essentially bypass authentication.
Johannes UllrichHOST
The result was that you could actually execute arbitrary code on any kind of Asterix server that was linked to an Isabel framework front end.

Sarah LaneHOST
[woshing sound] One shared key opens every Isabel door.
Sarah LaneHOST
VulnCheck says attackers are exploiting a critical Isabel framework flaw caused by the same hard-coded JWT signing key appearing in every installation.
Sarah LaneHOST
An unauthenticated attacker can forge a token and run operating system commands as the asterisk user.
Sarah LaneHOST
Isabel patched the flaw August 1st, and the Shadow Server Foundation first observed exploitation September 9th.

JustinHOST
So if you've got attacker, then we can say x poc actor colon attacker.
JustinHOST
So that they know, without having to inspect the JWT and see the email that's associated with it, what exactly is going on here.
JustinHOST
And the victim, likewise, should have a victim value for that header.
JustinHOST
And that will allow them to know which requests are being made as the victim.

Sarah LaneSOUNDBITE_SPEAKER
One shared key opens every Isabel door.
Sarah LaneSOUNDBITE_SPEAKER
Volnchak says attackers are exploiting a critical Isabel framework flaw caused by the same hard-coded JWT signing key appearing in every installation.
Sarah LaneSOUNDBITE_SPEAKER
An unauthenticated attacker can forge a token and run operating system commands as the asterisk user.
Sarah LaneSOUNDBITE_SPEAKER
Isabel patched the flaw August 1st, and the Shadow Server Foundation first observed exploitation September 9th.

speaker_1HOST
Very standard.
speaker_1HOST
When a user logs in legitimately, the server hands them a JWT.
speaker_1HOST
It acts almost like a like a digital VIP wristband at a club.
speaker_0HOST
OK, I like that analogy.
speaker_1HOST
So every time that user tries to access a protected area of the software, they just present the wristband.
speaker_0HOST
Right.
speaker_0HOST
And to prevent attackers from just, you know, printing their own fake VIP wristbands in their basement, JWTs have a built-in cryptographic signature.
speaker_1HOST
Exactly.
25 more episodes mention JSON Web Token.
Create an account to see the whole feed, search across every transcript, and follow the entities you care about.