Fuzzing
2
MENTIONS
2
EPISODES
2
PODCASTS
Search complete. 2 mentions across 2 episodes found for "Fuzzing".
Oct 1, 2026

Chris WysopalGUEST
And this has been the trend over cybersecurity for a really long time.
Chris WysopalGUEST
When a new class of tools comes out, if attackers are using that class of tools, they're going to have an advantage, like, say, fuzzers.
Chris WysopalGUEST
Fuzzers came out about 20 years ago, and it allowed attackers to find vulnerabilities that they couldn't find before just using, say, static analysis or code review.
Chris WysopalGUEST
And this fuzzing... found new bugs that defenders couldn't find unless they were using fuzzers themselves, right? So we've had these cycles of new tools have come out, offense has used them, and then eventually defense starts using them and we get sort of parity again.
Chris WysopalGUEST
So I think when we talk about AI, the same thing is going to happen.

Michael DyryndaHOST
A test for a parser might cover a valid string and an empty one.
Michael DyryndaHOST
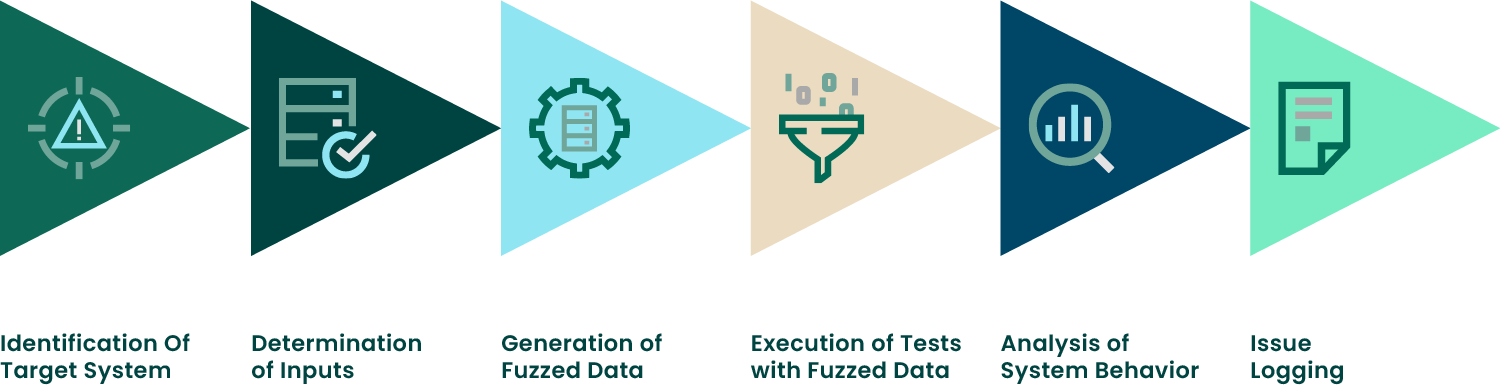
Fuzz testing searches for failures beyond those handwritten cases by generating inputs and passing them to your code.
Michael DyryndaHOST
With fuzz, which is a package by John Purvis, you can do this inside of Pest 5 Test.
Michael DyryndaHOST
The package uses Nikitsch's PHP fuzzer to change strings you provided and report any failures through Pest.