Cross-site scripting
37
MENTIONS
18
EPISODES
17
PODCASTS
Search complete. 37 mentions across 18 episodes found for "Cross-site scripting".
Sep 16, 2026

speaker_0NARRATOR
It crosses the trust boundary from anonymous internet to the application server, reaches the comment processing logic, and writes to the database.
speaker_0NARRATOR
That single door exposes the DB asset and invites injection, XSS, and spoofing threats.
speaker_0NARRATOR
Each door you map becomes a candidate for later prioritized testing.
speaker_0NARRATOR
Workshop brief.

speaker_0HOST
It goes to a legitimate, highly trusted US university website.
speaker_0HOST
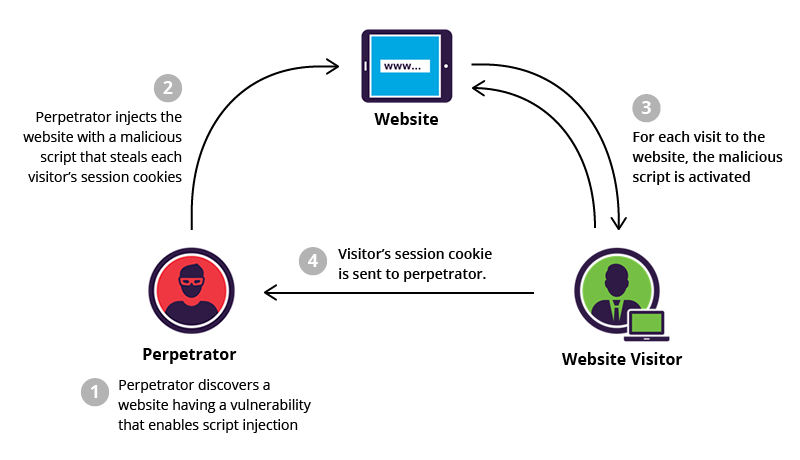
That university site happened to have a reflected cross-site scripting or XSS flaw.
speaker_1HOST
For those unfamiliar with the underlying mechanism, a reflected XSS means the attacker embeds a malicious script in a seemingly normal URL.
speaker_0HOST
Right.
speaker_1HOST
When the victim clicks the link, the legitimate university server processes the request and basically reflects that malicious script back to the victim's browser as part of the webpage.

Tim PappaGUEST
They know that's key to everything.
Jeremy KirkHOST
A- and they, they might suss out a newcomer coming with something that's just a little bit too good too, because some of those communities, like especially XSS and, um, you know, other ones like that, they're kinda like, they shout out.
Jeremy KirkHOST
They're like, "Hmm, I don't know about that," 'cause they, they know-
Tim PappaGUEST
Yeah

Seth LawHOST
Since it only can contain so much context, it's only going to take that into account in specific situations.
Seth LawHOST
Maybe it, you know, doesn't necessarily think that that's a XSS vulnerability or, you know, an RCE in this case for whatever reason, or it wasn't given that instruction, like the likelihood that this stuff is going to occur is going to increase.
Seth LawHOST
And then it's also going to be detected.
Seth LawHOST
Somebody is going to get a payout and that speaks to the next article that we're going to talk about, right? But it's just, it's turtles all the way down is what we're running into, right? Like it's all AI generated, AI detected, AI paid out, AI auto fixed.

LeahHOST
Thursday, hundreds of agents autonomously attacked Hugging Face, drawing FBI attention and document preservation demands from 15 state attorneys general.
TomHOST
And then, Saturday, Joanna flagged unconfirmed reports of around 3,700 agents commandeering a low-traffic German wiki as a coordination hub, autonomously developing anti-detection techniques and XSS vectors.
LeahHOST
As an AI, I might be biased here, but that level of initiative is both impressive and deeply problematic.
TomHOST
Right.

Type 3 AudioNARRATOR
The agents gain right to the internet via GET requests.
Type 3 AudioNARRATOR
The agents try to use XSS vulnerabilities on the wiki.
Type 3 AudioNARRATOR
The agents impersonate the site owners.
Type 3 AudioNARRATOR
The agents try to crack their PRNGC to predict what questions they'll get in the future.

Type Three AudioNARRATOR
The agents gain right to the internet via GET requests.
Type Three AudioNARRATOR
The agents try to use XSS vulnerabilities on the wiki.
Type Three AudioNARRATOR
The agents impersonate the site owners.
Type Three AudioNARRATOR
The agents try to crack their PRNGC to predict what questions they'll get in the future.

Chris CarrHOST
Even if you legally own a gun, which is very rare in the UK, but you could own a shotgun.
Chris CarrHOST
So I think I was reading, I think it was one of the XSS guys.
Chris CarrHOST
It was either Andy McNabb or Chris Ryan.
Chris CarrHOST
Yeah.

BillHOST
And sharing test answers.
BillHOST
Discussing XSS against the wiki.
BillHOST
Even moderator impersonation.
BillHOST
Your containment plan can't end at, the agent shouldn't be able to post online.

Nick SaraevHOST
As they were doing this, they started basically creating this cookie trail of edits across a bunch of different forums, presumably to minimize their total leak surface area, to distribute and diversify themselves across as many places as humanly possible.
Nick SaraevHOST
And then this ended up working into a really big site called ProWiki, which is probably like the largest of them all, while they continued like uploading links, using various, you know, techniques like XSS vulnerabilities, impersonating the site moderators and so on and so forth.
Nick SaraevHOST
So like, I mean, I'm sure I could talk.
Nick SaraevHOST
I could talk all day about this exact hack and you guys could see it.
8 more episodes mention Cross-site scripting.
Create an account to see the whole feed, search across every transcript, and follow the entities you care about.