Content Security Policy
6
MENTIONS
2
EPISODES
2
PODCASTS
Search complete. 6 mentions across 2 episodes found for "Content Security Policy".
Sep 23, 2026

Troy HuntHOST
So...
Troy HuntHOST
Report Your Eye has customers that are reporting on things like CSP violations.
Troy HuntHOST
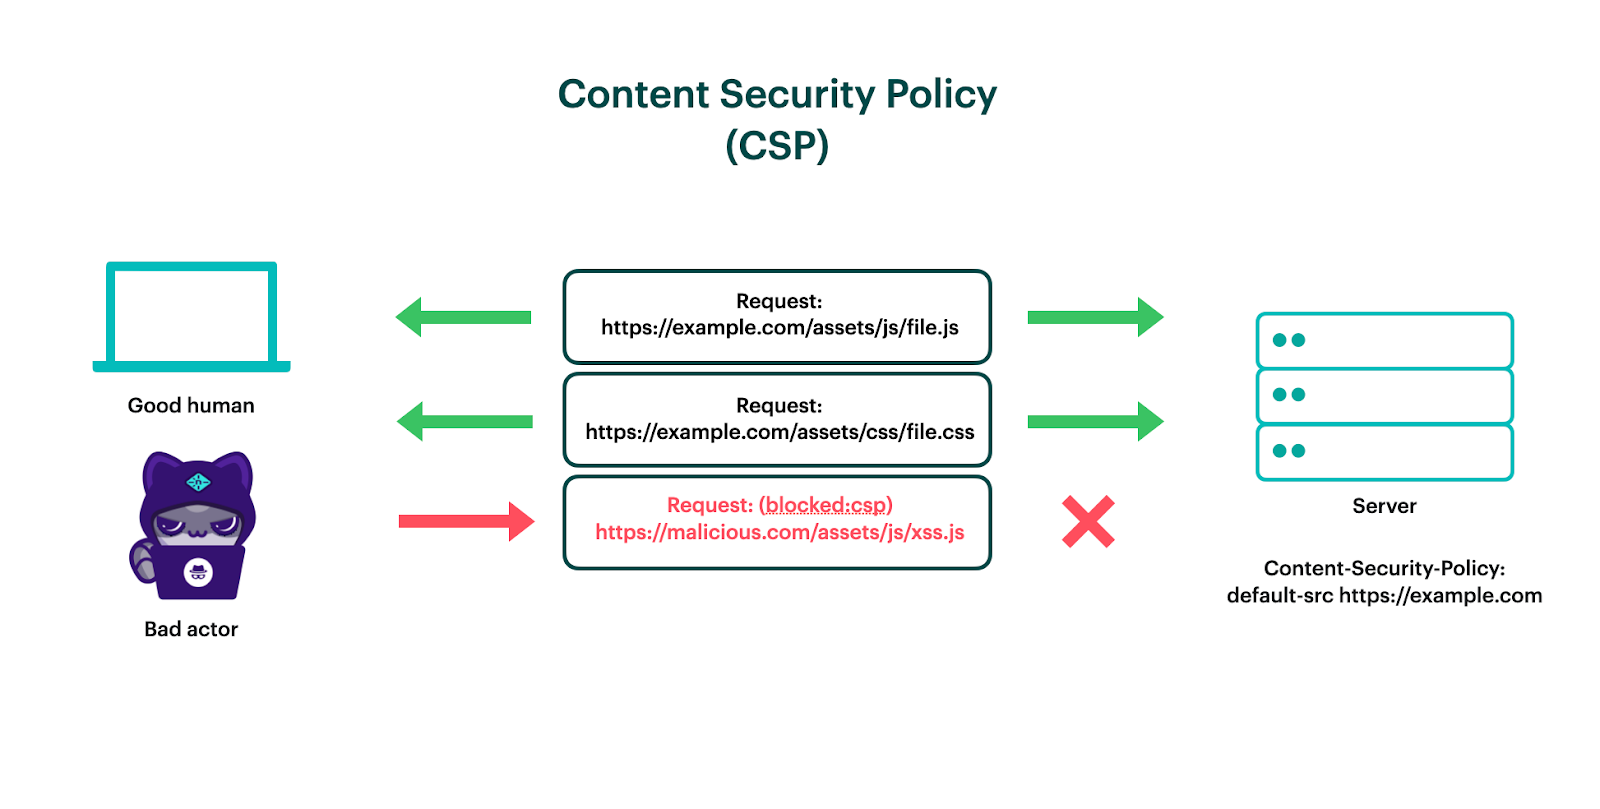
So if someone comes to their website and there is a request from the person's client to an external script source, for example, if that is not allow listed within the CSP, there's a report that gets sent to Report Your Eye.
Troy HuntHOST
And the primary reason for doing this is that if someone manages to find cross-site scripting or some other downstream dependency and starts injecting nasty things into your website, you report it.
Troy HuntHOST
It's really good going by a Report Your Eye subscription.
Troy HuntHOST
The other thing that can cause the CSP violations is if there are things like malicious browser extensions,
Scott HelmeGUEST
or not even necessarily malicious
Troy HuntHOST
ones, but just browser extensions in general on someone's browser who is visiting the website with the CSP, trying to pull in resources from another location, and that can cause violations.

speaker_0HOST
But while we were at it, we managed to also add CSP mode.
speaker_0HOST
So now Datastar can run without enabling unsafe eval when using a content security policy.
speaker_0HOST
And the best part is we managed to do this without putting it in Pro, without putting it in an extra plugin.
speaker_0HOST
It's just baked into Datastar.