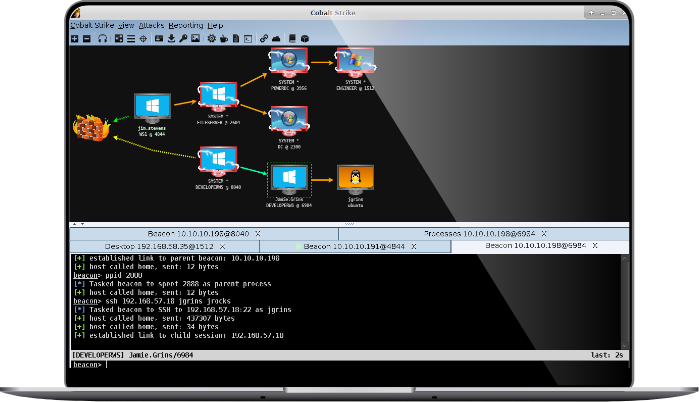
Cobalt Strike
SoftwareWikipedia
16
MENTIONS
7
EPISODES
7
PODCASTS
Search complete. 16 mentions across 7 episodes found for "Cobalt Strike".
Nov 12, 2026

Aurora BlumGUEST
Now, historically, we've seen a lot of cyber espionage and financially motivated threat actors taking advantage of pen testing or red teaming platforms that were originally built for security professionals.
Aurora BlumGUEST
So, for example, we've seen Cobalt Strike and Metasploit show up in intrusions, in malicious activity, as well as for legitimate use by pentesting themes.
Aurora BlumGUEST
Now, once you start mixing AI and agents into the mix, then you get a paradigm shift.
Aurora BlumGUEST
And this is what we are starting to see in the intrusions that we were reporting on, because now we're starting to see intrusions occurring at machine speed.
27 MINS LATER
Rohit NambiarGUEST
And I think LLMs are just going to make it so much more messier.
Luke McNamaraHOST
And it's not completely new.
Luke McNamaraHOST
I mean, the concept of I think, Aurora, you mentioned Cobalt Strike.
Luke McNamaraHOST
And I remember through that period where that was such a very commonly used tool across not just pen testers, not just criminal actors, various state sponsored groups.

Marc LaliberteHOST
There's like others in the space that are these, I mean, they're supposed to be for white hat hackers to do actual penetration testing, but they are
Ryan EstesGUEST
widely adopted by threat actors for malicious work tool like Metasploit, Cobalt Strike.
Ryan EstesGUEST
Cobalt Strike's the big one, yeah.
Marc LaliberteHOST
Exactly.
Marc LaliberteHOST
And so this seems like another one on the stack where it is clearly effective because threat actors have picked it up to start using it.

Christopher LuftHOST
In the newly identified attack, Frosty Neighbor targeted a Ukraine manufacturing company that plays an important role in the country's transportation sector.
Christopher LuftHOST
The attackers deployed Chisel, UltraVNC, Cobalt Strike, and a BB script-based wiper through Group Policy.
Christopher LuftHOST
ESET considers the operation significant because destructive cyber attacks in the region had previously been attributed to explicitly Russia-aligned actors.
Christopher LuftHOST
The incident represents an escalation from frosty neighbors' historically espionage-focused activities.
Matt BromileyHOST
Yeah, exactly.
Matt BromileyHOST
And then we get into the tools that they've been using and whatnot.
Matt BromileyHOST
Chisel, Ultra VNC, Cobalt Strike.
Matt BromileyHOST
Very, very typical tool set of a threat actor who, you know, probably operates very close to a state nexus threat actor if they are not an official state nexus threat actor.

Adrian CulleyHOST
it? On 155 of them, that's 10.6%, Census also found other threat tooling.
Adrian CulleyHOST
Cobalt Strike, VShell, Adaptix C2, other AI attack frameworks, all the usual suspects.
Adrian CulleyHOST
CyberStrike AI turns up alongside Artex on 70 hosts.
Adrian CulleyHOST
32 of open directories of attack tools.

Scott PoleyHOST
when it comes to what do you do when you've got the access, what do you do internally, that I don't see changing too much.
Scott PoleyHOST
Almost like a similar thing, but on the other side, remember when all those offensive tools like Cobalt Strike, Meterpreter, and Metasploit, all those kind of hit the scene.
Scott PoleyHOST
that was like a the other way where now it added a lot more technical capability to a lot of attackers but operationally they need to figure out that gap because just because you can get on a machine didn't mean you can do a lot with it if you didn't have a good operations behind it um to kind of hide who you are hide the activities or whatever it was kind of like a brute force but really technical swiss army knife i feel like this is like the inverse to that um And so that's going to be harder for defenders, I think, because with operational sophistication, it means there's going to be less like custom things necessarily, but a lot of things that are just built in, lay of the land, blending in better, so to speak, as far as capability-wise with the operation.
Scott PoleyHOST
But I think the one thing that we'll be telling is Will attackers, because it kind of lowers the bar a little bit if people want to get into the offensive space, will they be mature enough and experienced enough? Because just because you have the capability doesn't mean you understand the context for how to use it well.

Gerald AugerHOST
So if you're a threat actor, right? Like, let's pretend Devin Grady, for the sake of this discussion, is a threat actor.
Gerald AugerHOST
And Devin Grady loves using himself some Cobalt Strike.
Gerald AugerHOST
All right? He's a Cobalt Strike guy through and through.
Gerald AugerHOST
Get off my back, sliver.
Gerald AugerHOST
I'm Cobalt Strike for days.
Gerald AugerHOST
So the thing is, if we burn down Cobalt Strike, Devin Grady could use a different post-exploitation framework like Sliver, but that's going to be a pain in his butt because he's not familiar with it.
Gerald AugerHOST
It's like saying, for anyone in chat who's only used Windows computers, all of a sudden, we prevent you from using Windows.
Gerald AugerHOST
Yeah, you can use Linux or a Mac, but you'd have to get comfortable and it would produce challenge for you.

Prerna JoshiGUEST
So with persistence established, attackers, they seek higher level access moving from a regular user to an administrator or domain controller.
Prerna JoshiGUEST
right they exploit the privilege escalation vulnerabilities or they harvest the credentials with tools like mimic ads right and this phase allows the attacker to control the system and disable the defenses prepare for deeper infiltration right then there arrives your command and control so there is uh a very famous command and control framework which i uh always use cobalt strike but if you want to use a free one you can use sliver you can use posh c2 you can use mythic These are the famous ones, but you'll find a lot of them on GitHub or anywhere, right? But these are the most famous ones.
Prerna JoshiGUEST
The last three, Sliver, Posse2 and Mythic, these are free.
Prerna JoshiGUEST
There is Covenant as well, but Covenant is again, it's paid.
19 MINS LATER
Prerna JoshiGUEST
Right.
Prerna JoshiGUEST
Then weaponizing findings to gain an initial foothold.
Prerna JoshiGUEST
once vulnerabilities are identified red teams create or select payloads that safely demonstrate exploitation right so they use metasploit framework cobalt strike or their custom scripts to exploit the known cvs right weaponizing means turning a theoretical flaw into a controlled proof of concept for example using a privilege escalation exploit to gain admin access So the emphasis is on controlled execution, no data destruction, no persistence beyond scope and full documentation for later remediation.
Prerna JoshiGUEST
So in this screenshot, if you can see the image, in this image, it shows this process in action, searching for privilege escalation exploits across Windows, Linux, macOS and hardware platforms.