Change-advisory board
9
MENTIONS
3
EPISODES
2
PODCASTS
Search complete. 9 mentions across 3 episodes found for "Change-advisory board".
Sep 30, 2026

Rick DavisHOST
Returning to the podcast are IGES Corrections Advisory Committee experts, Rick Davis, Lina Yala, Jerry Breniger, and Krista Murray.
Rick DavisHOST
Together, the panel dives into how strong collaboration between the program team and Change Advisory Board can support a successful implementation, funding approaches that enable continuous improvement, and the importance of working closely with the solution providers to keep systems modern long after implementation.
Rick DavisHOST
Whether your agency is preparing for an OMS modernization effort or already navigating one, this episode offers plenty to consider.
Rick DavisHOST
Join the conversation and hear what these experts have learned about setting programs up for success today and into the future.
Rick DavisHOST
I am going to go back to being the moderator because Krista and Lynn and Jerry have definitely the hard part.
Rick DavisHOST
Answering questions is the hardest part of this whole podcast series.
Rick DavisHOST
So with that, Lynn, you brought up about the Change Advisory Board in a previous question.
Rick DavisHOST
Let me ask you this.

Sec GuyHOST
It is an operational governance framework that ensures changes are documented, rigorously tested, authorized, and auditable before they touch production.
Sec GuyHOST
At the center of this framework sits the Change Advisory Board.
Sec GuyHOST
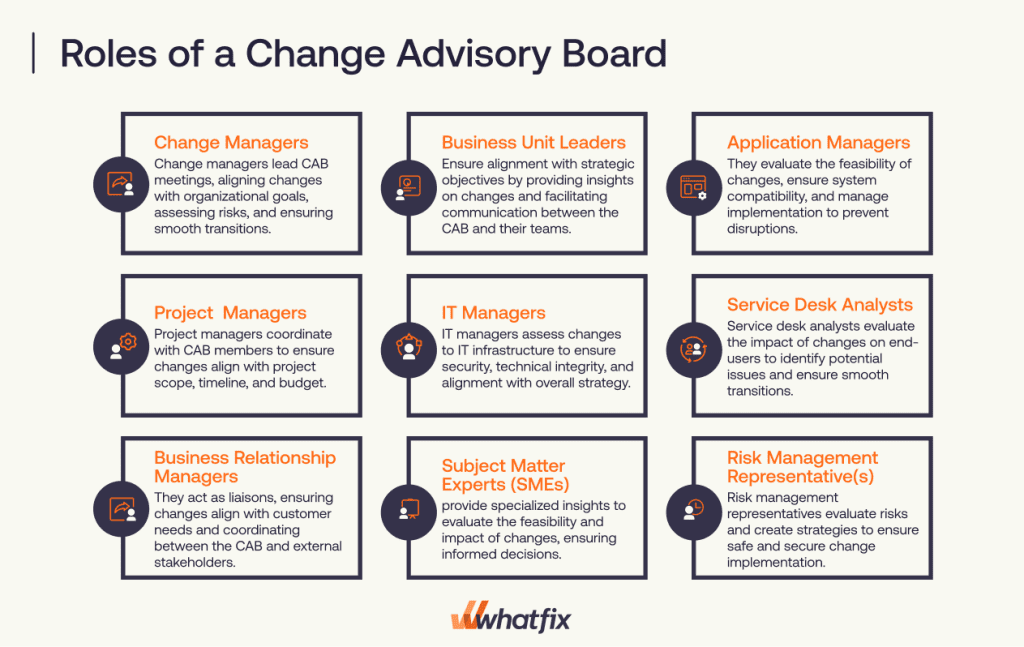
The Change Advisory Board is a cross-functional governing body made up of technical leads, infrastructure engineers, security personnel, and business managers.
Sec GuyHOST
Their mission is not to rubber stamp requests.
Sec GuyHOST
It is to evaluate the operational risk, security implications, and business disruption of any proposed modification to the enterprise environment.
Sec GuyHOST
The change owner must execute the change in an isolated staging or pre-production environment that mirrors production.
Sec GuyHOST
They must present verifiable proof that the patch closed the targeted vulnerability without breaking core business logic.
Sec GuyHOST
Once the Change Advisory Board evaluates the impact analysis and test results, the change is scheduled within a designated maintenance window.
Sec GuyHOST
In this workshop, you are the lead security architect for a national healthcare processing network.
Sec GuyHOST
At 8 o'clock this morning, the Change Advisory Board, or CAB, received an emergency change request from the infrastructure engineering team.
Sec GuyHOST
The proposal aims to overhaul the patient billing portal to improve query latency.
Sec GuyHOST
The request states, migrate back-end patient records to an external cloud database, update authentication endpoints, and bypass standard proxy inspection during the window to accelerate data sync.