Attribute-based access control
5
MENTIONS
3
EPISODES
3
PODCASTS
Search complete. 5 mentions across 3 episodes found for "Attribute-based access control".
Oct 6, 2026

Cory O'DanielGUEST
But if I only wanted to be able to manage one database, then I have to make it first, right? In AWS, I have to go make the database and then give it rights, right? And so one of the things I think that's going to be really crucial for an agent-centered world and development is many of the tools that we have today are RBAC-based, they're role-based.
Cory O'DanielGUEST
And I think that one thing that has to change is I think we're going to have to move towards like more classification-based permission systems like ABAC, where you can say, hey, this agent doesn't have the ability to create databases.
Cory O'DanielGUEST
It doesn't have the ability to manage that database properly.
Cory O'DanielGUEST
it has the ability to make non-PII stored Postgres databases in staging environments, right? And so you've given it its permissions based on a classification of what it's allowed to do.
Dan GerlancHOST
And are you actually using the agents as well to define what those policies should be, like converting them from here's a Jira ticket or company lore into this is what actually should be happening?
Cory O'DanielGUEST
Yeah, so, I mean, we do internally for sure, but customers definitely do as well.
Cory O'DanielGUEST
It's interesting, like, there's enough, like, There's enough compliance like zeitgeist in any of the LLMs where you can actually like expose how our ABAC system works and then say like the type of business that you are.
Cory O'DanielGUEST
And you'll actually see that Quad can spit out like a pretty good classification system for you, right? And so we have a lot of customers when they first come in, they'll get into like decision paralysis.

Bill AndersonGUEST
They're not humans, but we need to think about them in terms of their information transforming and information processing and carrying capabilities.
Bill AndersonGUEST
So we built the concept of users, resources, and actions, and that three tuple defines an ABAC policy, an attribute-based access control policy in Mattermost.
Bill AndersonGUEST
Am I allowed to do this thing? Am I allowed to join this conversation? Am I allowed to open this file? So we built that in.
Bill AndersonGUEST
The next step is you put that same concept around all of your resources.

Sec GuyHOST
This is the ultimate enforcement of the principle of least privilege.
Sec GuyHOST
Finally, we have the shift from RBAC to ABAC.
Sec GuyHOST
Role-based access just checks your job title, but attribute-based access control evaluates real-time context.
Sec GuyHOST
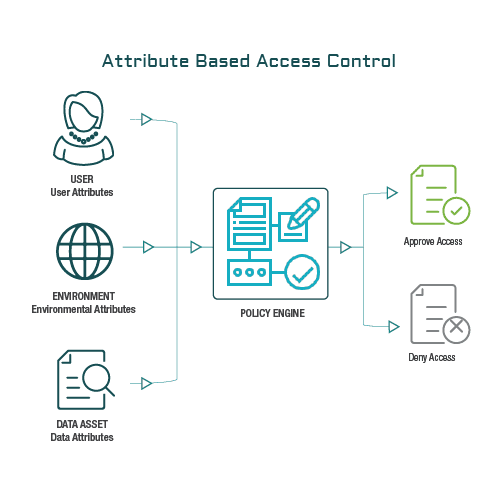
It looks at the user, the resource, and the environment.