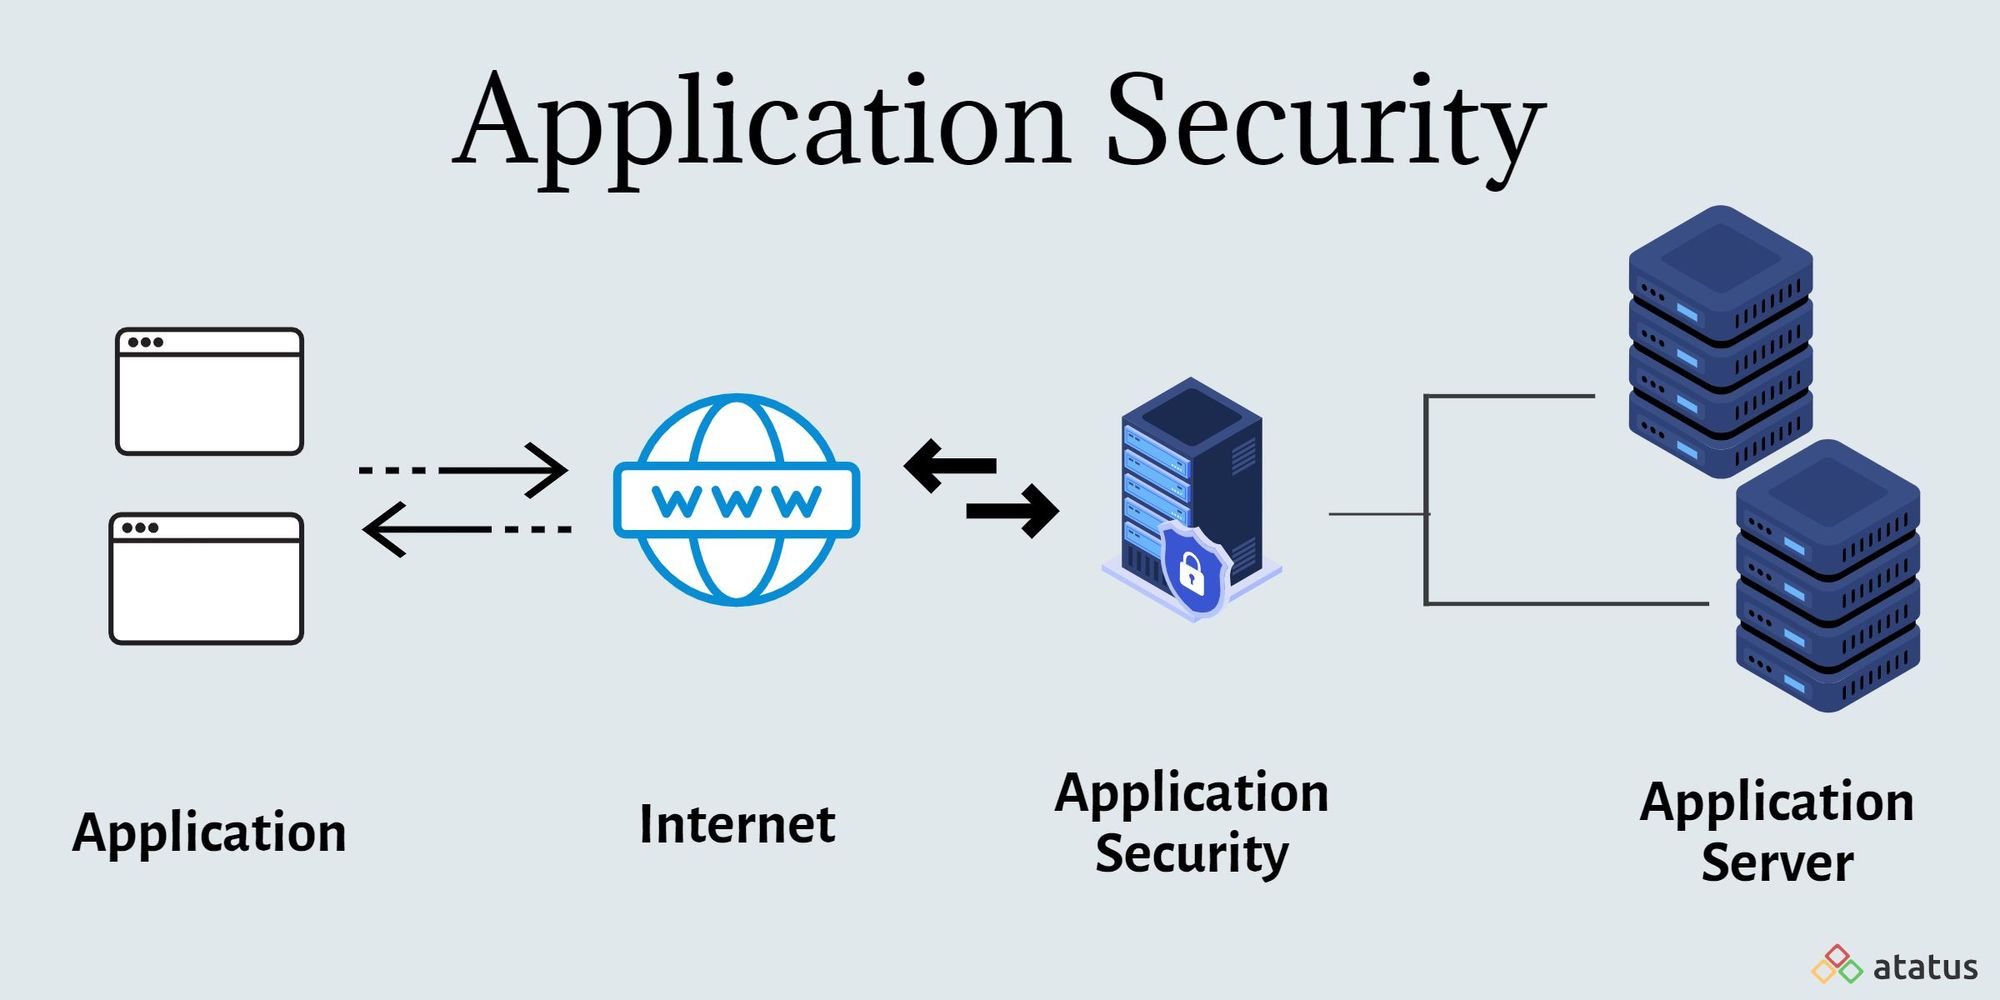
Application security
408
MENTIONS
70
EPISODES
45
PODCASTS
Search complete. 408 mentions across 70 episodes found for "Application security".
Oct 27, 2026

Mike ShemaHOST
Use your imagination and stay tuned for Application Security Weekly.
Mike ShemaHOST
It's the show to learn the latest tools and techniques to understand DevOps, applications, and the cloud.
Mike ShemaHOST
You're a trusted source for the latest AppSec news.
Mike ShemaHOST
It's time for Application Security Weekly.
Mike ShemaHOST
This is episode 406, recorded October 26, 2026.
41 MINS LATER
Rashid FerozeGUEST
For example, having your API inventory, having, hey, So that you can put better egress controls on the knuckles, on the firewalls.
Mike ShemaHOST
Yeah.
Mike ShemaHOST
And I think anytime you mentioned it can help with the inventory, my ears perk up because that is one of those things that for the last more than one decade, last two, if not three decades, that's a common starting point from an AppSec or security team that says, have an inventory of your applications, your microservices, your agents, for that matter, what have you, but that's so much easier said than done.

Mike SchemaHOST
Use your imagination and stay tuned for Application Security Weekly.
Mike SchemaHOST
It's the show to learn the latest tools and techniques to understand DevOps, applications, and the cloud.
Mike SchemaHOST
You're a trusted source for the latest AppSec news.
Mike SchemaHOST
It's time for Application Security Weekly.
Mike SchemaHOST
This is episode 406, recorded October 26, 2026.
41 MINS LATER
Rashid FerozeGUEST
For example, having your API inventory, having, hey, So that you can put better egress controls on the knuckles, on the firewalls.
Mike SchemaHOST
Yeah.
Mike SchemaHOST
And I think anytime you mentioned it can help with the inventory, my ears perk up because that is one of those things that for the last more than one decade, last two, if not three decades, that's a common starting point from an AppSec or security team that says, have an inventory of your applications, your microservices, your agents, for that matter, what have you, but that's so much easier said than done.

Mike ShemaHOST
Use your imagination and stay tuned for Application Security Weekly.
Mike ShemaHOST
It's the show to learn the latest tools and techniques to understand DevOps, applications, and the cloud.
Mike ShemaHOST
You're a trusted source for the latest AppSec news.
Mike ShemaHOST
It's time for Application Security Weekly.
Mike ShemaHOST
This is episode 406, recorded October 26, 2026.
40 MINS LATER
Rashid FerozeGUEST
So from a observability point of view, it has added a couple of pointers which other teams are consuming as well.
Rashid FerozeGUEST
For example, having your API inventory, having, hey, what are my servers talking to so that you can put better egress controls on the knuckles, on the firewalls.
Mike ShemaHOST
Yeah, I think anytime anytime you mentioned it can help with the inventory, my ears perk up because that is one of those things that for the last more than one decade, last two, if not three decades, that's a common, you know, starting point from an AppSec or security team that says, have an inventory of your applications, your microservices.

Mike SchemaHOST
Use your imagination and stay tuned for Application Security Weekly.
Mike SchemaHOST
It's the show to learn the latest tools and techniques to understand DevOps, applications, and the cloud.
Mike SchemaHOST
You're a trusted source for the latest AppSec news.
Mike SchemaHOST
It's time for Application Security Weekly.
Mike SchemaHOST
This is episode 406, recorded October 26, 2026.
40 MINS LATER
Rashid FerozeGUEST
So from a observability point of view, it has added a couple of pointers which other teams are consuming as well.
Rashid FerozeGUEST
For example, having your API inventory, having, hey, what are my servers talking to so that you can put better egress controls on the knuckles, on the firewalls.
Mike SchemaHOST
Yeah, I think anytime anytime you mentioned it can help with the inventory, my ears perk up because that is one of those things that for the last more than one decade, last two, if not three decades, that's a common, you know, starting point from an AppSec or security team that says, have an inventory of your applications, your microservices.

Fletus Poston IIIGUEST
So I took the team from 5 to 15, then left them in 22, went to an endpoint backup and recovery after a carve-out, built out their security program.
Fletus Poston IIIGUEST
When I left them in 24, I was their acting deputy CISO, servicing AppSec, TVM, SecOps, etc.
Fletus Poston IIIGUEST
Now I serve as the director of IT and cybersecurity for an additive 3D manufacturing company called 3D Systems.
Fletus Poston IIIGUEST
We print, we build and print 3D printers for commercial use.
Phil HowardHOST
I have a few developer friends, believe it or not, and they really, to get real deep on the philosophy of just like, of the, you building out the project before you touch anything, kind of the whole like, What's your thoughts there? Like, how do you guys go about that before even?
Fletus Poston IIIGUEST
That is a hot topic, both academic and professionally.
Fletus Poston IIIGUEST
For people who followed anything, AppSec was something I picked up in my last role because we're a software development company.
Fletus Poston IIIGUEST
I learned very quickly the importance of plan, build, run, even as even not just thinking from a security point of view.

Ashish RajanHOST
Because the way we are developing code today, where basically the amount of code being published into a GitHub or a GitLab repository is just so enormous.
Ashish RajanHOST
AppSec people are already under the pressure and this tiny little thing, which is always assumed that, hey, someone somewhere had done a threat modeling in the beginning and then followed up with a pen test exercise right at the end of it to make sure that those gaps were never missed.
Ashish RajanHOST
It's slowly being questioned whether it should exist in the old way.
Ashish RajanHOST
So in this episode, I had Ben Oster from Threatmodeler.ai. We were talking about the need for change to how threat modeling is done and what is possible with AI today.

Stephanie ZavalaGUEST
Same thing for cybersecurity.
Stephanie ZavalaGUEST
There's AppSec, there's CloudSec, there's Incident Response, there's Red Team, right? And then there is GRC that sometimes falls under security and IT as well.
Stephanie ZavalaGUEST
So you just have to be at least high level versed on what this market that you're operating in is.
Stephanie ZavalaGUEST
And maybe AI can just give you the general overview.

Sean MartinHOST
I'm just wondering, is there a way to take what you have done and, well, I'll say this first.
Sean MartinHOST
They employ AppSec people.
Sean MartinHOST
They employ network engineers.
Sean MartinHOST
They employ endpoint managers to handle these different areas.

Sean MartinHOST
I'm just wondering, is there a way to take what you have done and, well, I'll say this first.
Sean MartinHOST
They employ AppSec people.
Sean MartinHOST
They employ network engineers.
Sean MartinHOST
They employ endpoint managers to handle these different areas.

Carissa BreenHOST
Let's go back to your comment like everyone will do a little kind of a little bit of everything.
Carissa BreenHOST
Do you think it'll just get to a point in the future, whereas historically it's development teams have been in a silo and security or AppSec or whatever you want to call it have sort of had their own team.
Carissa BreenHOST
Do you envision, given your role in this space, it'll just become like one sort of big team and then people really specialize in an area? What are your sort of thoughts given everything you're doing here at Datadog, but just the industry in general and where it's headed?
Olivier PomelGUEST
Yeah, I mean, I will preface it by saying it's hard to predict exactly where it's going because we're all getting up to speed with the tools, the agents.
60 more episodes mention Application security.
Create an account to see the whole feed, search across every transcript, and follow the entities you care about.