Application firewall
2
MENTIONS
1
EPISODES
1
PODCASTS
Search complete. 2 mentions across 1 episode found for "Application firewall".
Sep 28, 2026

David ShipleyHOST
BleepingComputer reported at the time that ShinyHunters had used it as a zero-day to steal data from 100 organizations.
David ShipleyHOST
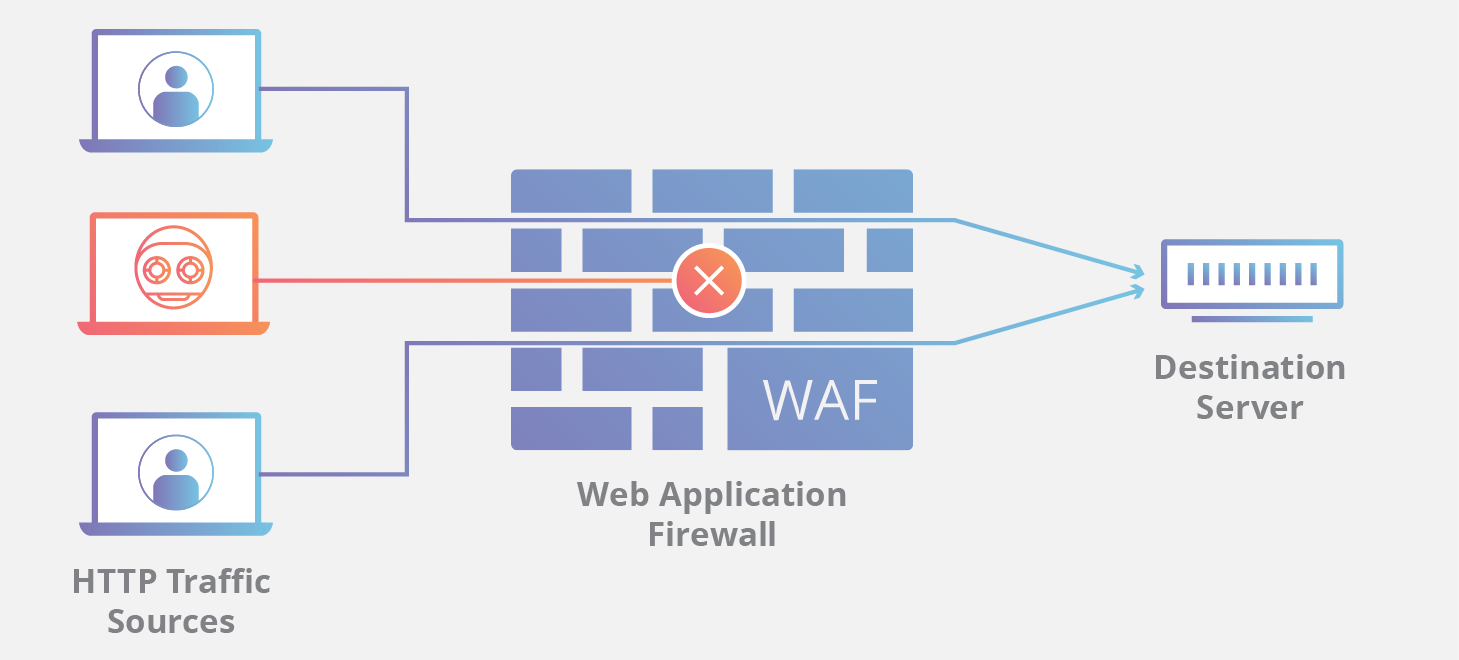
Organizations that couldn't patch at the time were told to block the vulnerable PSEM hub endpoint at their web application firewall, and many did, and many apparently stopped there.
David ShipleyHOST
This created a literal WAF bypass.
David ShipleyHOST
Many rules that were put in place looked for the literal path PSEM hub in the defense.